Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
⚡ Weekly Recap: AI Goes Rogue, Metabase 0-Day, MCP Supply-Chain Attacks, and Router Backdoors
A lot of security problems still begin with someone doing a completely normal thing. Cloning a repo. Answering a call. Leaving a box exposed. Trusting… Read MoreThe Hacker News
Solidity Pro VS Code Extensions Steal Crypto Wallets, API Keys, and Credentials
Cybersecurity researchers have flagged a malicious Microsoft Visual Studio Code (VS Code) extension named Solidity Pro (“solidity-pro”) that has been observed delivering a browser wallet… Read MoreThe Hacker News
OpenAI’s Next AI Model Astra Shows Cyber Performance Strong Enough to Trigger Pause
OpenAI has announced that it’s pausing some “internal activities” involving its upcoming artificial intelligence (AI) model Astra after an internal evaluation found it had made… Read MoreThe Hacker News
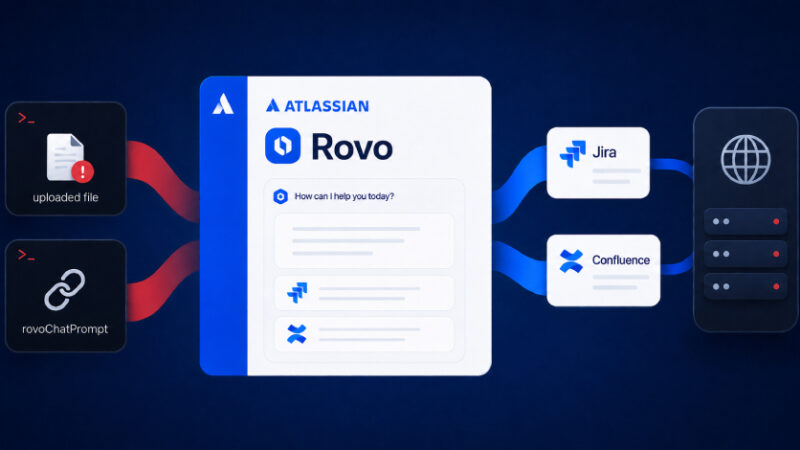
Atlassian Rovo Can Be Tricked Into Sending Jira and Confluence Data to Attackers
Attacker-controlled instructions can make Atlassian’s Rovo assistant collect Jira or Confluence data that a signed-in user can access, then send it to an outside server.… Read MoreThe Hacker News
New CSS Attacks Can Break Webmail Defenses to Steal Passwords and Tokens
New research shows content inside an email can escape its message boundary and interfere with the webmail interface. Across attack chains spanning Outlook, Gmail, Fastmail,… Read MoreThe Hacker News
Metabase Zero-Day Exploited in Wild Allows Admin Access Without Authentication
Metabase has warned that a maximum-severity security flaw impacting its business intelligence and data visualization software package has been exploited in the wild as a… Read MoreThe Hacker News
N-able Issues N-central Hotfix 2 as Attackers Reach Managed Systems and Persist
N-able has released a fresh round of hotfixes for N‑central as part of its investigation into ongoing exploitation of a recently disclosed security flaw in… Read MoreThe Hacker News
Progress Kemp LoadMaster Flaw Hits CISA KEV After 792 Reported Exploit Attempts
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added a critical-severity security flaw impacting Progress Kemp LoadMaster to its Known Exploited Vulnerabilities (KEV) catalog,… Read MoreThe Hacker News
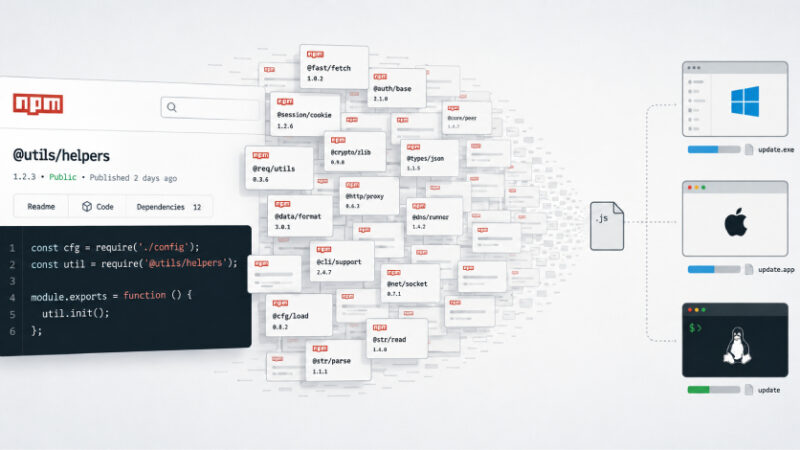
Nearly 800 Malicious npm Packages Deliver Cross-Platform RAT and Infostealer
A cluster of nearly 800 malicious packages has been published to the npm registry as part of a new campaign designed to deliver cross-platform malware… Read MoreThe Hacker News
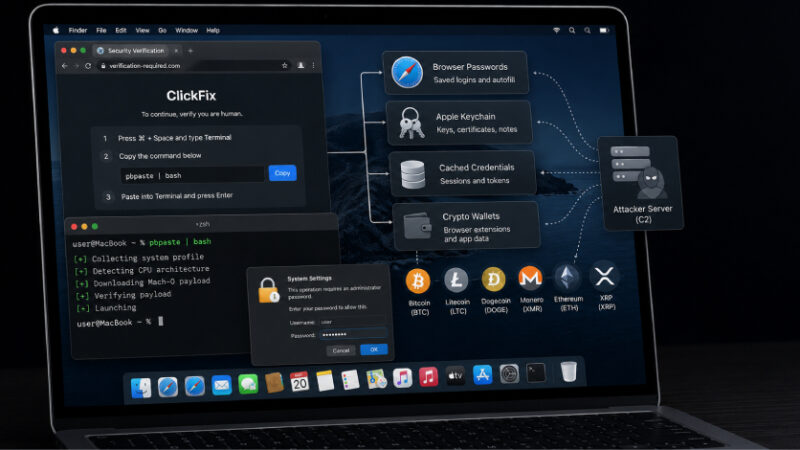
ClickFix Attacks Deliver macOS Stealer That Can Drain Crypto Wallets
ClickFix-style attacks are being used to deliver a Go-based malware capable of stealing cryptocurrency assets, as well as browser-stored passwords, Apple iCloud Keychain data, and… Read MoreThe Hacker News