Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days
A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the… Read MoreThe Hacker News
Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks
Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed… Read MoreThe Hacker News
An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.
The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR… Read MoreThe Hacker News
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
A flaw in Linux’s vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of… Read MoreThe Hacker News
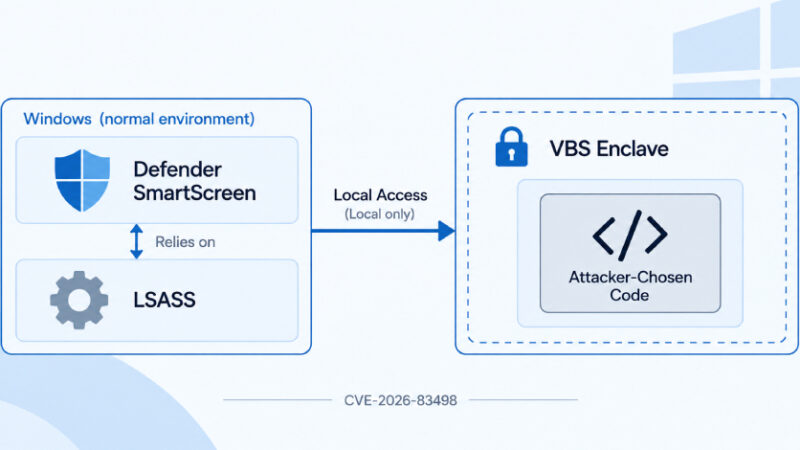
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the… Read MoreThe Hacker News
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Three vulnerabilities in LG’s webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a… Read MoreThe Hacker News
Product Walkthrough: Bitdefender AI Visibility and Control
A user opens a browser tab, pastes data into a chat assistant, and nothing is installed. A developer adds a coding assistant as an editor extension,… Read MoreThe Hacker News
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to… Read MoreThe Hacker News
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
Two of 31 newly disclosed flaws in Progress Software’s MarkLogic Server database could let an account given only some management privileges take administrator control of the server,… Read MoreThe Hacker News
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code… Read MoreThe Hacker News