Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of… Read MoreThe Hacker News
Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population… Read MoreThe Hacker News
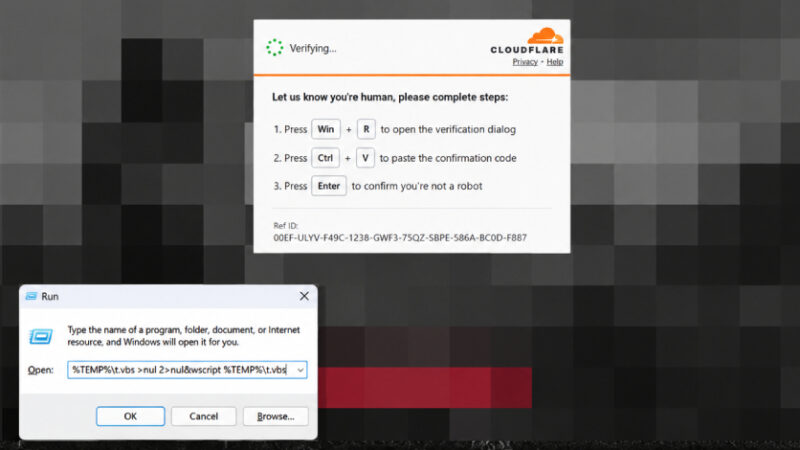
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead… Read MoreThe Hacker News
Apple Plans Tighter macOS Full Disk Access Controls Over AI Agent Data Access
Apple has announced that it’s taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by… Read MoreThe Hacker News
Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS… Read MoreThe Hacker News
New NetScaler Zero-Day Exploited in Targeted Attacks Can Knock SAML Deployments Offline
Citrix has released security updates for a high-severity security flaw in NetScaler ADC and Citrix NetScaler Gateway that has been exploited as part of targeted… Read MoreThe Hacker News
ShinyHunters Suspect Rey Reportedly Detained in Jordan, Helping FBI Identify Group Members
A suspected member of the ShinyHunters digital extortion group, who goes by the online alias “Rey,” has been allegedly detained by authorities in Jordan, Reuters… Read MoreThe Hacker News
China-Aligned TA419 Targets U.S. AI Policy Experts With Microsoft AitM Phishing
A new China-nexus cyber espionage group known as TA419 has been attributed to multiple credential phishing campaigns targeting artificial intelligence (AI) experts working for U.S.… Read MoreThe Hacker News
MI5 Says China’s MSS Funded Research Involving 100+ U.K.-Linked Academics
The U.K.’s domestic intelligence and security agency has warned that more than 100 academics have helped China boost its intelligence gathering efforts on behalf of… Read MoreThe Hacker News
Warlock Exploits SharePoint Flaws to Disable Security Tools and Deploy Ransomware
The suspected China-linked threat actor known as Warlock is still continuing to weaponize Microsoft SharePoint vulnerabilities, likely both old and new, in attacks targeting organizations… Read MoreThe Hacker News