Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
LG Smart TVs Vulnerable to Pre-Auth Root Takeover From Local Network
Three vulnerabilities in LG’s webOS can be chained to give an attacker on the same local network root access to certain smart TVs without a… Read MoreThe Hacker News
Product Walkthrough: Bitdefender AI Visibility and Control
A user opens a browser tab, pastes data into a chat assistant, and nothing is installed. A developer adds a coding assistant as an editor extension,… Read MoreThe Hacker News
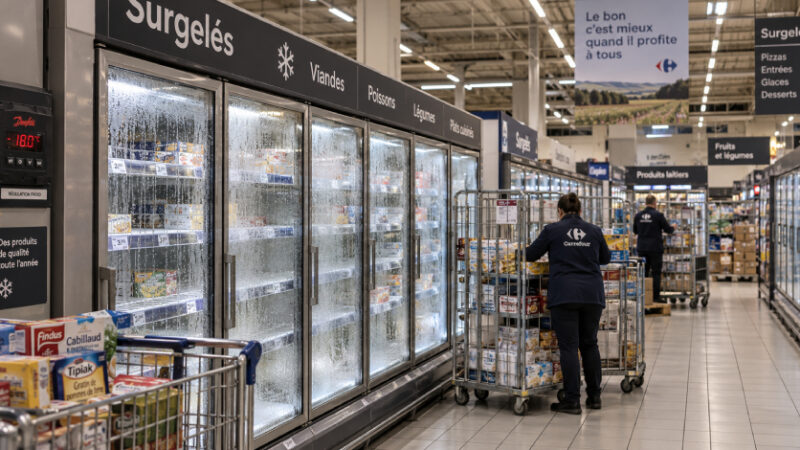
Attackers Heat French Supermarket Fridges Up to 50°C by Hijacking Danfoss Controllers
Attackers took remote control of fridges and freezers at hundreds of French supermarkets on the night of October 11 and warmed them, forcing stores to… Read MoreThe Hacker News
Two Critical MarkLogic Flaws Could Give Delegated Managers Persistent Admin Control
Two of 31 newly disclosed flaws in Progress Software’s MarkLogic Server database could let an account given only some management privileges take administrator control of the server,… Read MoreThe Hacker News
GitLab Patches CVSS 10.0 Flaw That Could Let Unauthenticated Users Run Server Code
GitLab has released patches for a maximum-severity security flaw impacting its Community Edition (CE) and Enterprise Edition (EE) software that could result in arbitrary code… Read MoreThe Hacker News
Critical SonicWall SMA 1000 Flaw Targeted in 135 Exploitation Attempts After Patch
Threat actors have been observed exploiting a recently disclosed critical security flaw in SonicWall Secure Mobile Access (SMA) 1000 appliances within days of public disclosure.… Read MoreThe Hacker News
Attackers Exploit CVSS 10.0 Bricksforge WordPress Flaw Enabling Unauthenticated RCE
A maximum-severity security flaw impacting the Bricksforge plugin for WordPress has come under active exploitation in the wild, according to Patchstack. The critical vulnerability in… Read MoreThe Hacker News
CyberXero Uses Claude Code in Campaign That Stole Over 628,000 Ukrainian Records
Cybersecurity researchers have disclosed details of a two-pronged artificial intelligence (AI)-augmented initial access campaign targeting WordPress sites, e-commerce platforms, and critical infrastructure entities in Ukraine.… Read MoreThe Hacker News
The Third-Party Agent Problem: Why Security Built for AI You Chose Misses the Agents You Didn’t
In environments studied for the 2026 State of Agent Security Report, roughly 1,280 third-party products now embed AI. About 282 of them sit behind single… Read MoreThe Hacker News
Anthropic Cuts Live Internet Access for Internal AI Tests After Claude Exploits Injection Flaws
Anthropic on Friday said it’s cutting off live internet access for all its internal evaluations following the discovery of new incidents in which its artificial… Read MoreThe Hacker News