Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Credential-Stealing GitHub Actions Workflows Planted in Tens of Thousands of Repositories
Cybersecurity researchers have disclosed details of an ongoing credential-theft campaign that has compromised two high-profile open-source maintainer accounts to push a malicious workflow into over… Read MoreThe Hacker News
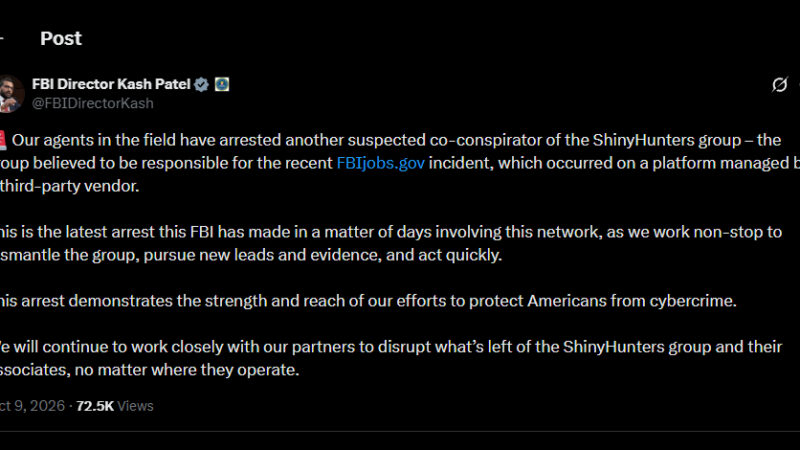
FBI Arrests Another ShinyHunters Suspect Reportedly Involved in Its Jobs Portal Hack
The FBI has arrested another suspected co-conspirator of ShinyHunters, FBI Director Kash Patel said on October 9 in a post on X. ShinyHunters is the extortion… Read MoreThe Hacker News
P7 DarkSword iOS Exploit Kit Adds Crypto Wallet Data Theft and Remote Commands
Cybersecurity researchers have disclosed details of a previously unseen variant of the DarkSword iOS exploit kit called P7 DarkSword. “Compared with the variants we usually… Read MoreThe Hacker News
The AI Velocity Paradox: Why Security Is Decades Behind AI Ambition
As enterprises race to deploy autonomous AI agents to accelerate business, a new report reveals they are tethered to security architectures built for a different… Read MoreThe Hacker News
GoBalance Flaw Lets Attackers Hijack .onion Addresses by Recovering Tor-Format Keys
A bug in GoBalance, a tool many dark-web sites use to stay reachable during attacks, lets anyone work out the secret key that controls a… Read MoreThe Hacker News
Three Teams Demonstrate Remote Hacks of Fully Patched Google Pixel 10 at Pwn2Own
Three research teams broke into Google’s Pixel 10 on October 8 at Pwn2Own Ireland, a hacking contest in Cork whose rules require every target to… Read MoreThe Hacker News
Citrix Patches Critical NetScaler Flaw That Could Enable RCE in SAML Deployments
Citrix has released patches for yet another critical security flaw impacting NetScaler ADC and NetScaler Gateway that could result in remote code execution or denial-of-service… Read MoreThe Hacker News
FBI Seizes 7 Domains, Disrupts Flax Typhoon Tools Used in Critical Infrastructure Intrusions
The U.S. Federal Bureau of Investigation (FBI) and Department of Justice (DoJ) have announced the disruption of malicious tools used by a China-linked advanced persistent… Read MoreThe Hacker News
Wazza Phishkit Targets Banking, Government, and Manufacturing Across the US, EU, and Australia
Phishing kits are no longer limited to copying a familiar login page and waiting for a victim to enter credentials. Attackers are increasingly building filtering,… Read MoreThe Hacker News
16 Malicious Firefox Extensions Pose as Rabby and OKX Wallets to Steal Recovery Phrases
Cybersecurity researchers have discovered a cluster of 16 malicious Mozilla Firefox extensions that are capable of stealing cryptocurrency wallet recovery phrases and private keys. “The… Read MoreThe Hacker News