Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
CISA Flags Three Linux Kernel Vulnerabilities Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added three security flaws impacting the Linux kernel to its Known Exploited Vulnerabilities (KEV) catalog,… Read MoreThe Hacker News
Public Exploits Released for Four Linux Kernel Flaws That Enable Local Root
A security researcher has released working exploit code for four Linux kernel flaws that each let a local user gain root, the highest level of… Read MoreThe Hacker News
Claimed Bug Bounty Hunter Likely Used LLM to Build PhantomRaven npm Stealer
A financially motivated threat actor has been linked to the development and distribution of a JavaScript (JS)-based information stealer known as PhantomRaven via the npm… Read MoreThe Hacker News
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that’s assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered… Read MoreThe Hacker News
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point’s Security Management and Log Servers could allow an attacker without login credentials to run code as root on those… Read MoreThe Hacker News
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools,… Read MoreThe Hacker News
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere… Read MoreThe Hacker News
Attackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command Execution
A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability in… Read MoreThe Hacker News
Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports… Read MoreThe Hacker News
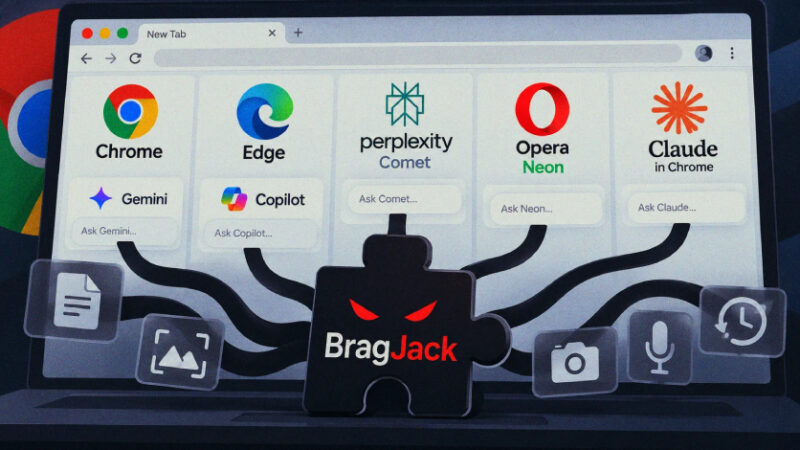
One Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and Claude
Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in… Read MoreThe Hacker News