Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Nimbus Manticore Expands Toolset With TWOSTROKE-Like Backdoor and SSH Tunneler
Cybersecurity researchers have discovered additional infrastructure and previously undocumented malware associated with Nimbus Manticore, an Iranian state-sponsored hacking group affiliated with the Islamic Revolutionary Guard… Read MoreThe Hacker News
NovaCookies Campaigns Abuse Genuine Docusign Notifications to Steal Microsoft 365 Sessions
Cybersecurity researchers have disclosed details of a new adversary-in-the-middle (AitM) phishing toolkit called NovaCookies that’s used as a proxy to redirect Microsoft 365 sign-ins, while… Read MoreThe Hacker News
INTERPOL Operation Jackal IV Arrests 58, Identifies 263 in Global Cyber Fraud Crackdown
An eight-month INTERPOL operation targeting West African organized crime groups has led to arrests of 58 people and the identification of 263 suspects. “The operation,… Read MoreThe Hacker News
Newly SLEEPWALKER Backdoor Waits for One Crafted Packet, Then Runs Its Own Bytecode
An independent malware researcher has documented a previously unreported Windows backdoor, dubbed SLEEPWALKER, that stays inert in memory until a specifically crafted network packet reaches… Read MoreThe Hacker News
Critical Gitea RCE Actively Exploited as Reported Attack Drops Miner-Like Payload
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Tuesday warned of active exploitation efforts targeting a recently patched critical security flaw impacting Gitea. The… Read MoreThe Hacker News
Fake Apple Support AI Calls Target Stolen-Device Owners for Passcodes and 2FA Codes
Cybersecurity researchers have disclosed details of a phishing-as-a-service (PhaaS) platform built to strip Apple’s Activation Lock from stolen devices, using rented AI voice agents that… Read MoreThe Hacker News
U.S. Sanctions Iran-Linked Hackers Behind Critical Infrastructure Breaches
The U.S. Department of the Treasury has announced fresh sanctions on Iranian cyber actors as part of what it called an “unprecedented, whole-of-government, economic campaign”… Read MoreThe Hacker News
Actively Exploited Oracle WebLogic Flaw Lets Unauthenticated Attackers Access Critical Data
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Monday added a maximum-severity security flaw impacting Oracle HTTP Server and Oracle WebLogic Server to its… Read MoreThe Hacker News
Shipping More AI Code Than You Can Secure? Watch How to Control Remediation Debt
If your developers are using AI coding tools, you are probably already seeing the upside: faster development, more code, and less time spent on routine… Read MoreThe Hacker News
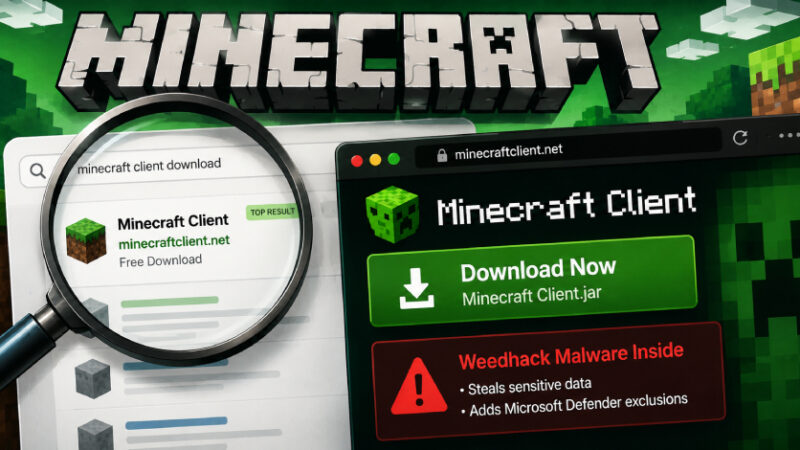
Weedhack Malware Spreads via Fake Minecraft Clients and SEO Poisoning
Cybersecurity researchers have found that several websites are still actively distributing a malware family known as Weedhack to gamers by masquerading as Minecraft clients. McAfee… Read MoreThe Hacker News