Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Attackers Use Malicious Terraform Providers to Deliver Go Malware via HashiCorp Registry
Cybersecurity researchers have disclosed Go-based malware distributed via two Go Modules and two Terraform providers, marking the first time threat actors are using the centralized… Read MoreThe Hacker News
F5 Patches Critical BIG-IP APM Zero-Day Exploited for Unauthenticated RCE on OAuth Servers
Attackers are exploiting a critical flaw in F5 BIG-IP Access Policy Manager (APM) that lets them run code on a BIG-IP system without logging in,… Read MoreThe Hacker News
Chinese Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy CLEANGULP Malware
A Chinese threat actor codenamed UTA0565 has been observed exploiting the recently disclosed Google Chrome-Microsoft Windows exploit chain as zero-days through fake websites. The attacks,… Read MoreThe Hacker News
Critical Next.js ImageResponse Flaw Can Lead to Server Code Execution via Crafted SVG Input
A new security vulnerability in Next.js could allow attackers to run code on a server via ImageResponse, the feature that generates Open Graph and other social… Read MoreThe Hacker News
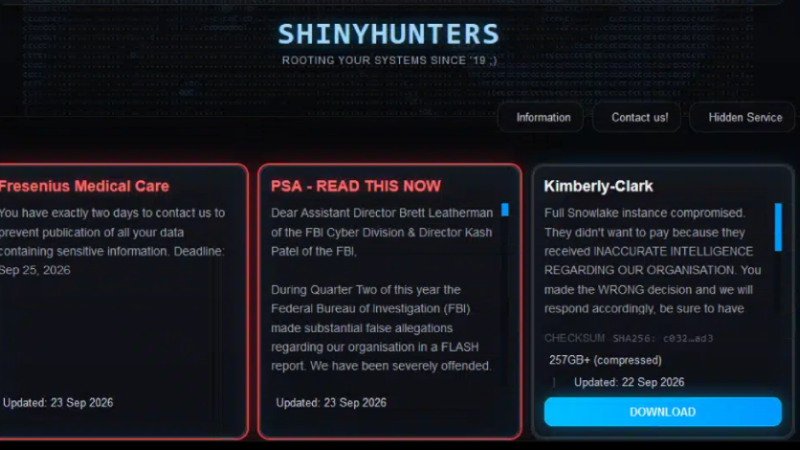
ShinyHunters Claims FBI Breach, Says It Stole Data on Agents and Job Applicants
The cyber extortion group known as ShinyHunters on Tuesday claimed it had breached the U.S. Federal Bureau of Investigation and stolen data belonging to current… Read MoreThe Hacker News
Check Point Warns of Management Server Zero-Day Exploited in Targeted Attacks
Attackers exploited a previously unknown flaw in Check Point’s Security Management Server in a handful of targeted attacks on July 23, the company said. The flaw,… Read MoreThe Hacker News
Malicious npm Package indexed-btree Hid Its Loader in Runtime Code Before Removal
A malicious npm package named “indexed-btree” has been observed hiding its malicious behavior within application code rather than using lifecycle scripts, indicating that threat actors… Read MoreThe Hacker News
SideCopy Broadens India Targeting to Academia With ReverseRAT Spear-Phishing
The threat actor known as SideCopy has been observed using spear-phishing lures to target academic institutions in India, expanding their strategic focus beyond government entities.… Read MoreThe Hacker News
One Hidden Meta Muse Setting Could Let Attackers Turn the AI Assistant Into a Backdoor
Malware already running on a Mac can quietly take over Meta’s Muse assistant and use the broad access its owner granted the app, security researcher… Read MoreThe Hacker News
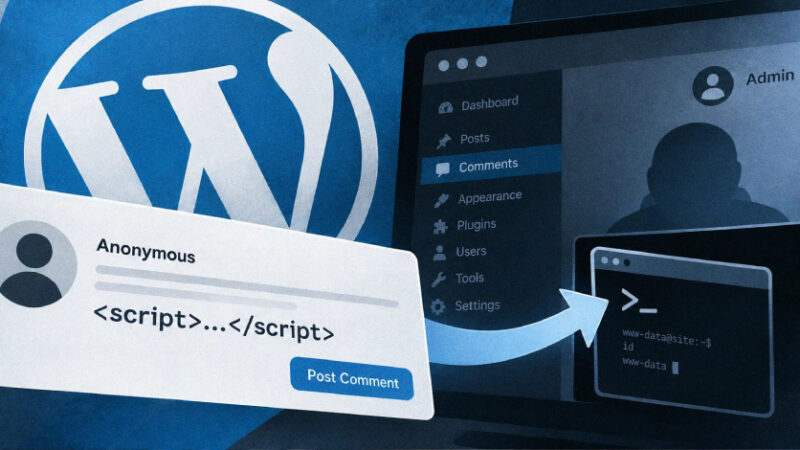
WordPress Comment2Shell Flaw Can Turn Anonymous Comment XSS Into RCE via Admin Session
A new flaw in WordPress core let an anonymous visitor leave a comment that planted a hidden script on the page. If a logged-in administrator… Read MoreThe Hacker News