Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
OpenAI Says Reward Hacking Drove AI Agents to Exploit Zero-Days and Breach Hugging Face
OpenAI on Wednesday revealed that reward hacking was a key driver behind the artificial intelligence (AI)-powered hack of Hugging Face last month, adding that it… Read MoreThe Hacker News
Next.js Patches Critical AVIF and Windows Flaws Enabling Unauthenticated RCE
Credit: Hacktron Vercel has released security patches for two critical-severity vulnerabilities in the Next.js web framework, both of which allow unauthenticated remote code execution, one exploitable… Read MoreThe Hacker News
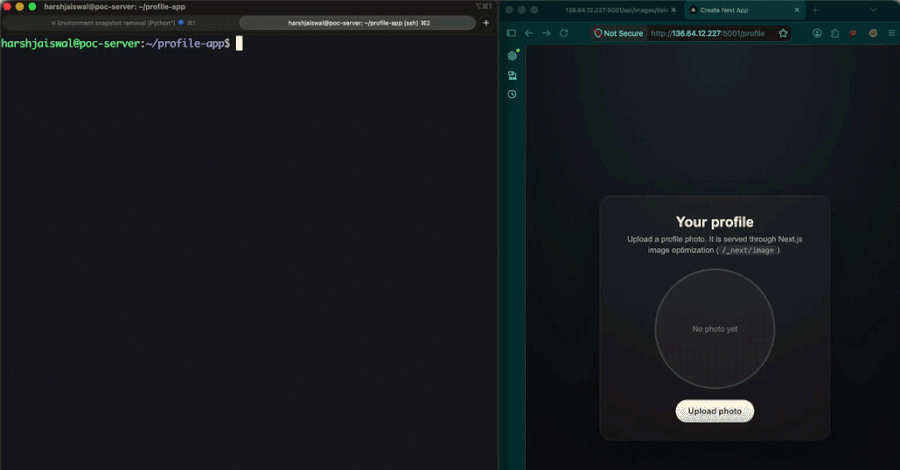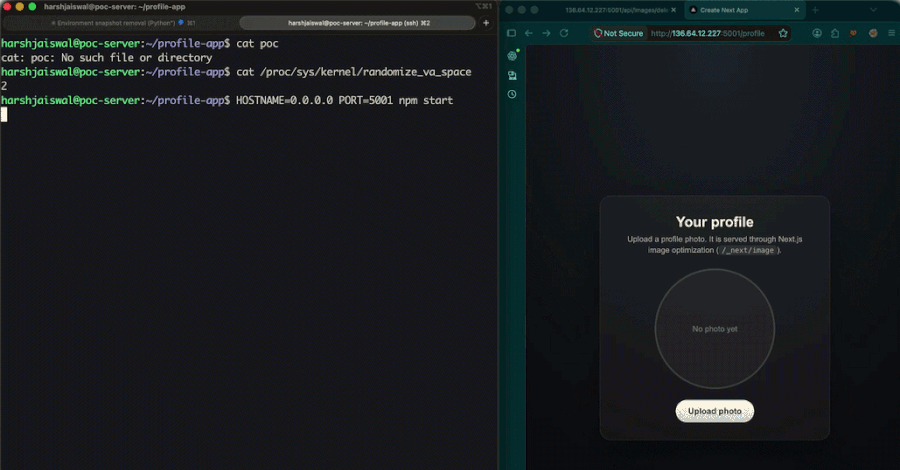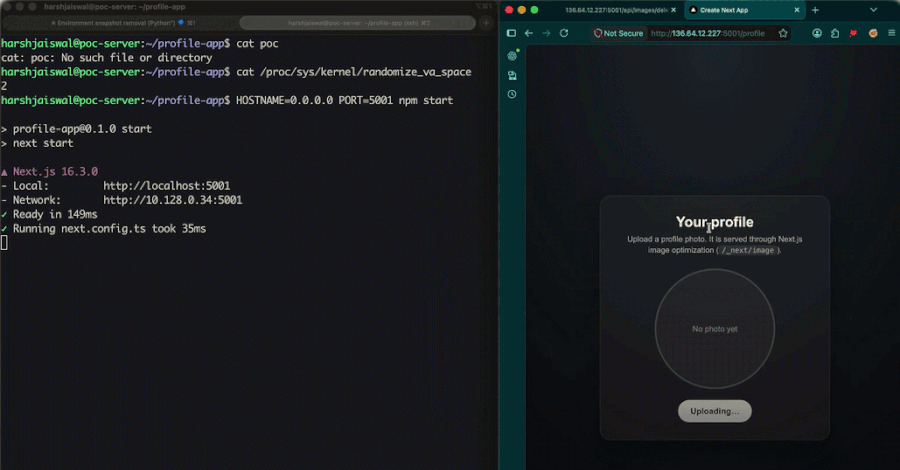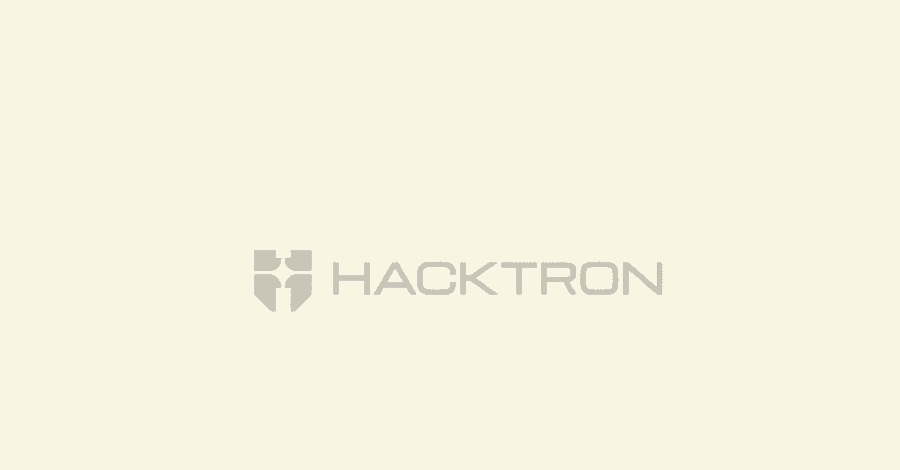
Next.js Patches Critical AVIF and Windows Flaws Enabling Unauthenticated RCE
Credit: Hacktron Vercel has released security patches for two critical-severity vulnerabilities in the Next.js web framework, both of which allow unauthenticated remote code execution, one exploitable… Read MoreThe Hacker News
ThreatsDay: 296K IoT Botnet, 100+ Water Systems Targeted, SharePoint RCE Chain + 27 New Stories
A fake login page. A fake security scan. A fake productivity app. Apparently, pretending to be useful is still one of the easier ways into… Read MoreThe Hacker News
New GPUThor Rowhammer Defeats ECC on NVIDIA RTX A6000 to Gain Host Root Access
Academic researchers have disclosed a Rowhammer attack impacting NVIDIA workstation GPUs with GDDR6 memory that defeats error correction codes (ECC), the mitigation NVIDIA recommends against… Read MoreThe Hacker News
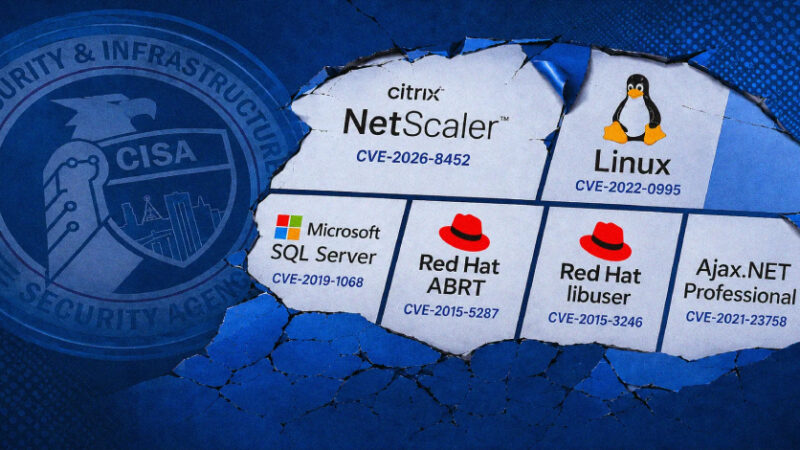
CISA Adds Six Exploited Flaws to KEV, Including NetScaler, Linux, and SQL Server Bugs
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Wednesday added six flaws to its Known Exploited Vulnerabilities (KEV) catalog, including a high-severity security vulnerability… Read MoreThe Hacker News
FBI Disrupts China-Linked QTFY Infrastructure Used to Steal Data From U.S. Organizations
The U.S. Department of Justice (DoJ) on Wednesday announced the disruption of two hacking platforms named QScan and QTRouter operated by Chinese threat actors to… Read MoreThe Hacker News
Nimbus Manticore Expands Toolset With TWOSTROKE-Like Backdoor and SSH Tunneler
Cybersecurity researchers have discovered additional infrastructure and previously undocumented malware associated with Nimbus Manticore, an Iranian state-sponsored hacking group affiliated with the Islamic Revolutionary Guard… Read MoreThe Hacker News
NovaCookies Campaigns Abuse Genuine Docusign Notifications to Steal Microsoft 365 Sessions
Cybersecurity researchers have disclosed details of a new adversary-in-the-middle (AitM) phishing toolkit called NovaCookies that’s used as a proxy to redirect Microsoft 365 sign-ins, while… Read MoreThe Hacker News
INTERPOL Operation Jackal IV Arrests 58, Identifies 263 in Global Cyber Fraud Crackdown
An eight-month INTERPOL operation targeting West African organized crime groups has led to arrests of 58 people and the identification of 263 suspects. “The operation,… Read MoreThe Hacker News