Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
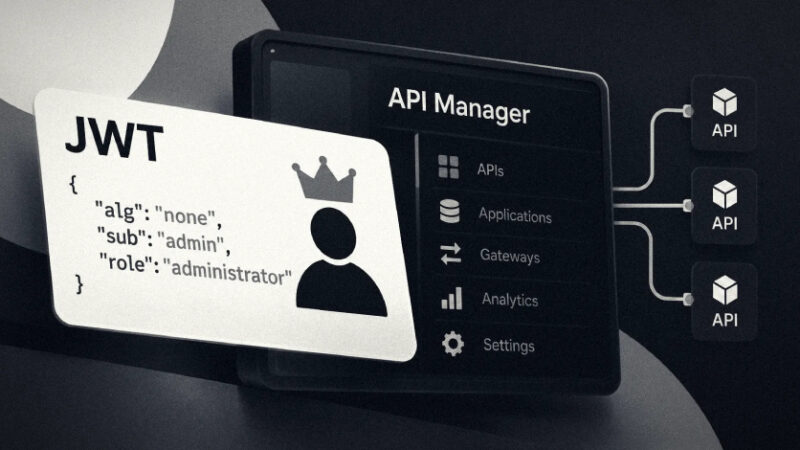
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as… Read MoreThe Hacker News
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the… Read MoreThe Hacker News
Iranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists
Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran’s intelligence service uses to… Read MoreThe Hacker News
BambooToken Malware Uses MQTT to Control Windows and Linux Systems
Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows… Read MoreThe Hacker News
LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server
A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory… Read MoreThe Hacker News
Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution
Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The… Read MoreThe Hacker News
China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE
A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver… Read MoreThe Hacker News
New DDRop Attack Breaks Intel TDX and AMD SEV-SNP Confidential Computing
Researchers have disclosed a new hardware attack, called DDRop, that breaks the memory protection in Intel and AMD confidential computing by silently dropping writes to… Read MoreThe Hacker News
3BB Attacker Used MeshCentral Backdoor for Root Access, Targeted Subscriber Credentials
An attacker was operating inside the network of 3BB, one of Thailand’s largest broadband providers, and maintained remote control of internal machines using a legitimate… Read MoreThe Hacker News
Malicious Twitch Browser Extension Leaks OAuth Tokens From Nearly 31,000 Users
A malicious cross-store Twitch browser extension has leaked OAuth tokens associated with nearly 31,000 users to proxy servers operated by a Russian commercial bot service.… Read MoreThe Hacker News