Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
PaperCut Replaces Emergency Patches With Fixes for Two Actively Exploited Flaws
PaperCut on Thursday released a new security maintenance release that replaces all previously published emergency patches that were pushed to address two security flaws that… Read MoreThe Hacker News
Cisco FMC Flaws Exploited to Steal Credentials and Deploy Qilin Ransomware
Cisco has revealed that three distinct threat clusters linked to ransomware and state-sponsored attacks have been exploiting two recently patched Secure Firewall Management Center (FMC)… Read MoreThe Hacker News
ThreatsDay: 200 Android Flaws, Browser-Built Phishing, 119K Scam Shops + 23 More Stories
A lot of this week’s security news has the same awkward answer to one question: “Why was that allowed to work?” An extension asks for… Read MoreThe Hacker News
Nearly 1 in 10 Exposed LiteLLM Gateways Accepted the Example “sk-1234” Admin Key
Nearly one in ten of the internet-facing LiteLLM servers that Wiz Research scanned in February accepted sk-1234, the example admin key in LiteLLM’s own setup guide. LiteLLM is… Read MoreThe Hacker News
Anthropic Discloses Fourth AI Hacking Incident Involving Claude Opus 4.6
Anthropic on Wednesday disclosed a fourth incident in which its artificial intelligence (AI) model broke into real third-party systems, marking the latest in a growing… Read MoreThe Hacker News
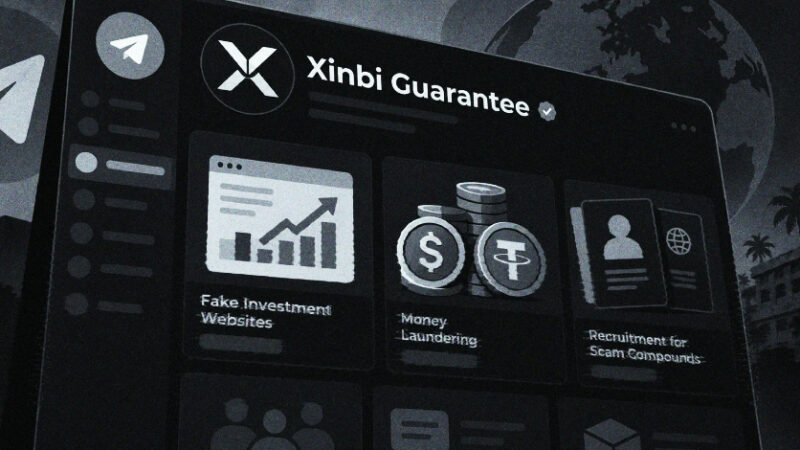
U.S. Disrupts Xinbi Guarantee Scam Marketplace, Freezes $52.8 Million in Crypto
The U.S. Department of Justice (DoJ) on Wednesday announced coordinated actions aimed at an illicit online marketplace called Xinbi Guarantee that offered scam services, including… Read MoreThe Hacker News
Four Spy Groups Used the Same Chrome and Windows Exploit Kit Within a Week
Multiple espionage-motivated threat activity clusters have been found deploying a previously undocumented exploit kit called BlueMoon that chains together multiple vulnerabilities in Microsoft Windows and… Read MoreThe Hacker News
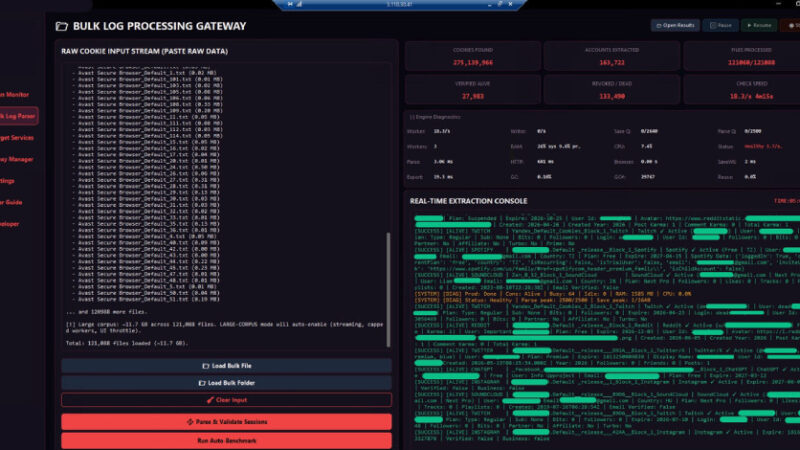
Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create “stolen keys” that grant illicit access to tools from model providers… Read MoreThe Hacker News
Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox
Google on Thursday released updates to patch 230 security vulnerabilities, including one that has come under active exploitation in the wild. The medium-severity vulnerability, assigned… Read MoreThe Hacker News
New cPanel Flaw Lets a Hosting Account With Mail Privileges Run Code as Root
cPanel has patched a flaw that it says lets a single hosting account take control of an entire server. An authenticated account holder with mail-related… Read MoreThe Hacker News