Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
F5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk Scans
Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk,… Read MoreThe Hacker News
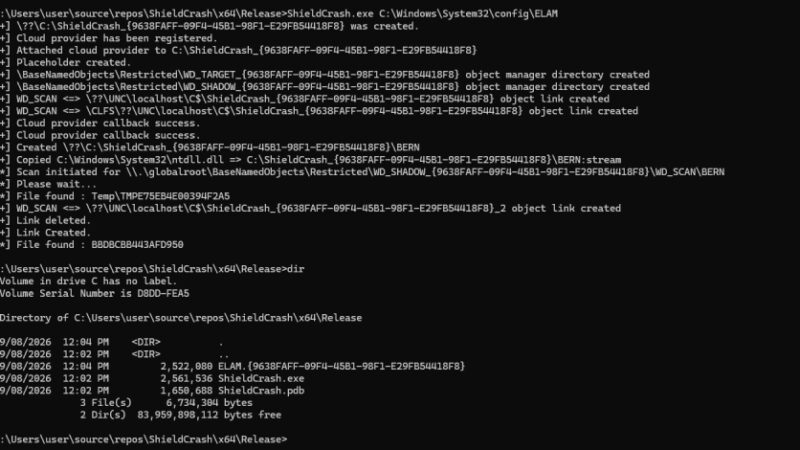
Researcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be Bypassed
The security researcher known as Chaotic Eclipse has dropped a proof-of-concept (PoC) for yet another zero-day in Microsoft Defender. The vulnerability, codenamed ShieldCrash, is assessed… Read MoreThe Hacker News
SAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code Execution
SAP has released security updates to address multiple vulnerabilities, including a maximum-severity flaw in SAP Extended Passport (EPP) Processing that could have a severe impact… Read MoreThe Hacker News
Adobe Patches Magento Zero-Day Exploited to Deploy Rust Backdoor and PHP Web Shell
Adobe on Monday released security patches to address a maximum-severity flaw impacting Adobe Commerce and Magento Open Source that has come under active exploitation in the wild.… Read MoreThe Hacker News
BengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support Scams
Cybersecurity researchers have disclosed details of a sprawling search engine optimization (SEO) poisoning campaign that paves the way for malware deployment and tech support scams.… Read MoreThe Hacker News
Grindr to Pay £26 Million to Settle U.K. Claims Over HIV Status Data Sharing
Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it shared users’… Read MoreThe Hacker News
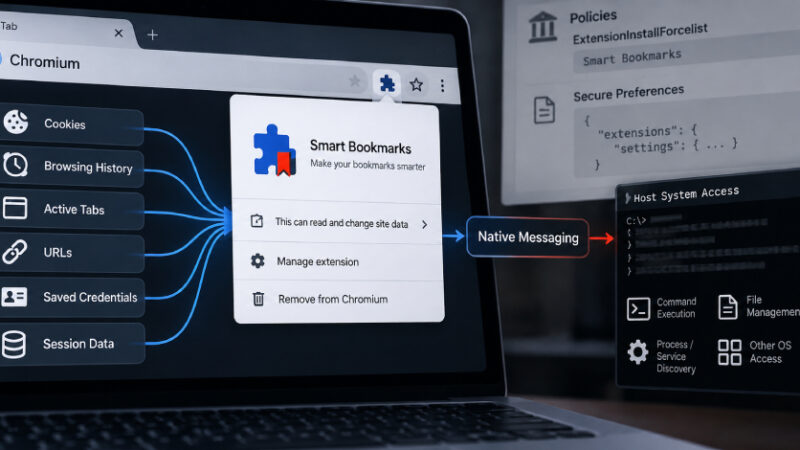
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. “Requiring prior… Read MoreThe Hacker News
Fake IT Calls Target Executives in Microsoft 365 Data Theft and Extortion Attacks
Threat hunters have disclosed details of a widespread data theft and extortion threat cluster that’s targeting Microsoft 365 and other software-as-a-service (SaaS) offerings through information… Read MoreThe Hacker News
N-able Issues Fourth N-central Hotfix in Five Weeks for Unauthenticated RCE Flaw
Every on-premises N-central build below 2026.3.1.14 — including servers updated to Hotfix 3 a day earlier — needs Hotfix 4. N-able’s incident notice says the… Read MoreThe Hacker News
JSCeal Malware Can Bypass Google Authentication Using Stolen Session Cookies
Cybersecurity researchers have unpacked JSCeal, a sophisticated compiled V8 JavaScript (JSC) malware with credential harvesting, surveillance, and traffic-interception capabilities. “The payloads are protected with javascript-obfuscator,… Read MoreThe Hacker News