Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
RatHat Android Malware Abuses ADB to Retain Shell Access After Uninstall
Cybersecurity researchers have flagged a new Android malware called RatHat that’s assessed to be operated by China-based threat actors and features an artificial intelligence (AI)-powered… Read MoreThe Hacker News
Critical Check Point Management Flaw Lets Unauthenticated Attackers Run Code as Root
A critical vulnerability in Check Point’s Security Management and Log Servers could allow an attacker without login credentials to run code as root on those… Read MoreThe Hacker News
ThreatsDay: Self-Rewriting Agents, 800+ Flaws Patched, Insider SIM Swaps and 22 More New Stories
Attackers keep finding new keys. The funny part is that defenders keep inventing where to store them. This week, those keys sit in AI tools,… Read MoreThe Hacker News
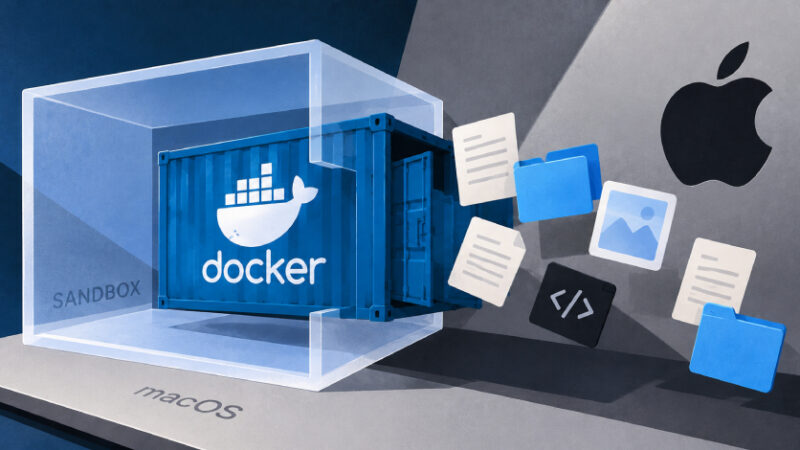
Critical Docker Sandboxes Flaw Lets Malicious Guest Code Read and Modify macOS Host Files
Malicious code running inside a Docker Sandboxes virtual machine on macOS could escape the project directory shared into it and read or change files anywhere… Read MoreThe Hacker News
Attackers Exploit Issabel Framework Flaw Enabling Unauthenticated OS Command Execution
A critical security flaw in Issabel Framework, a web-based framework for the open-source unified communications PBX software, has come under active exploitation. The vulnerability in… Read MoreThe Hacker News
Three Threat Groups Target Russian Enterprises With Backdoors, Ransomware, and Wipers
Enterprises in Russia have emerged as the target of three threat activity clusters tracked as NightEagle, Hacking Cat, and Toy Ghouls, according to multiple reports… Read MoreThe Hacker News
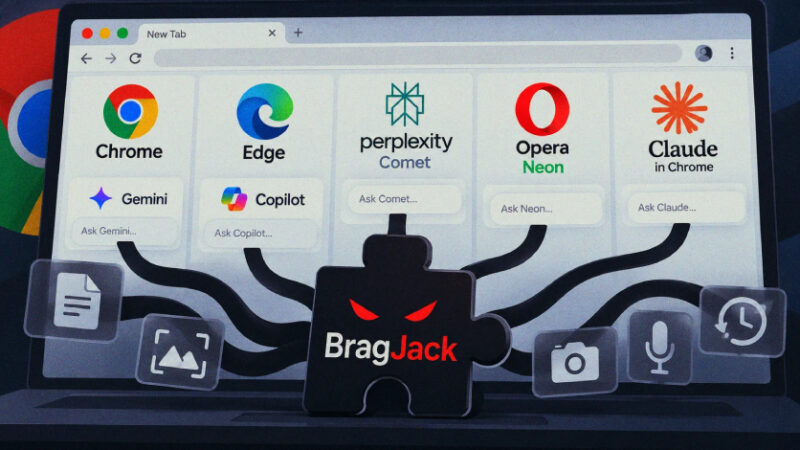
One Extension Could Hijack AI Assistants Across Chrome, Comet, Edge, Opera Neon and Claude
Security researchers at Forever Security have shown that one ordinary browser extension could take control of the AI assistants built into five Chromium-based products: Gemini Live in… Read MoreThe Hacker News
Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories
Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories. Before the… Read MoreThe Hacker News
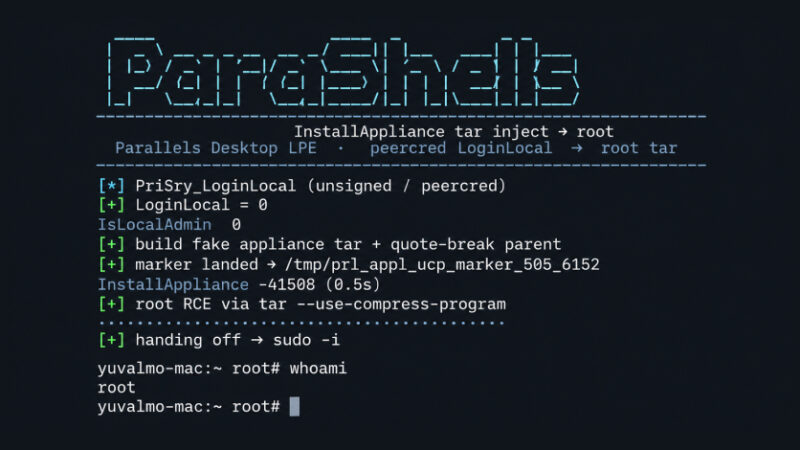
Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install Fix
Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac,… Read MoreThe Hacker News
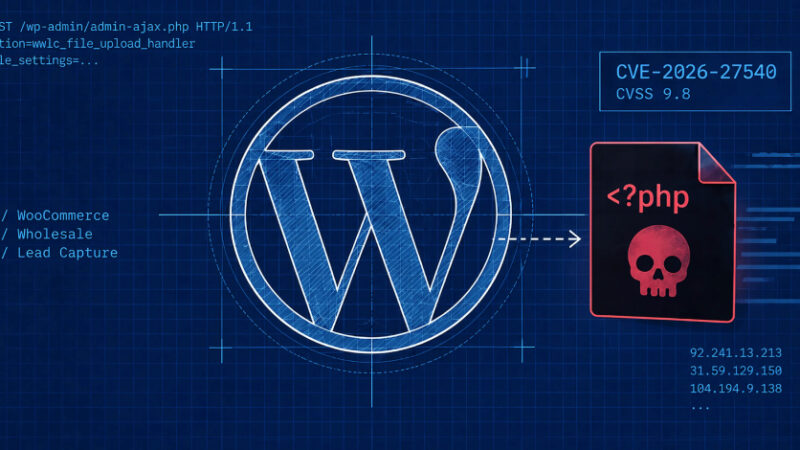
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This… Read MoreThe Hacker News