Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Attackers Use Passkey Phishing to Hijack Microsoft Cloud Accounts and Exfiltrate Data
Microsoft has disclosed details of two campaigns in which threat actors are abusing third-party email delivery infrastructure to blast financial fraud scam messages and using… Read MoreThe Hacker News
CISA Adds 5 Actively Exploited Artifactory, ScreenConnect, and RouterOS Flaws to KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five security flaws impacting JFrog Artifactory, ConnectWise ScreenConnect, and MikroTik RouterOS to its Known Exploited… Read MoreThe Hacker News
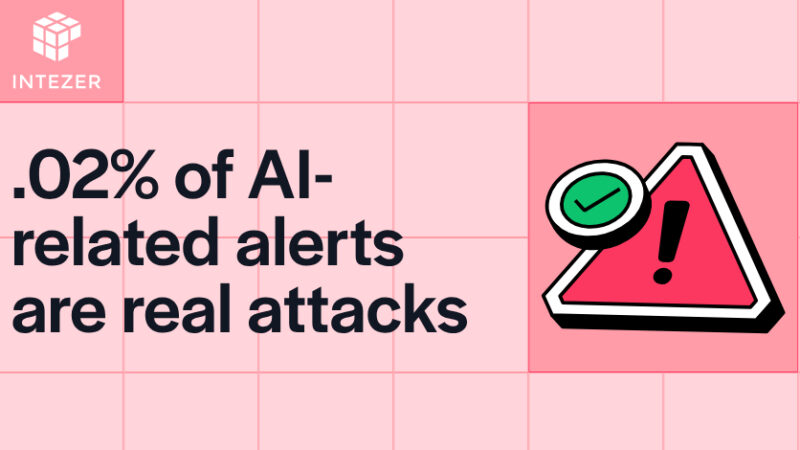
When the Whole Company Adopts AI: What It Does to Your SOC
Over the past year, we watched a new class of alert appear in enterprise security operations centers and grow faster than anything else in the… Read MoreThe Hacker News
OpenAI Agents Linked to RubyGems Campaign That Gained RCE on RubyDoc Servers
The “major malicious attack” that targeted RubyGems in May 2026 was the work of a swarm of OpenAI agents, according to a new report published… Read MoreThe Hacker News
GitLab CVSS 10 File-Read Flaw Draws In-the-Wild Probes After Disclosure
GitLab has released patches to address multiple flaws, including a maximum-severity security vulnerability that has witnessed in-the-wild probes within hours of public disclosure. The vulnerability… Read MoreThe Hacker News
Anthropic Says Seven China-Based AI Labs Ran Industrial-Scale Claude Distillation Attacks
Anthropic on Thursday said it identified and disrupted industrial-scale illicit distillation attacks against Claude from seven labs based in China, including Alibaba, Moonshot, DeepSeek, Z.ai… Read MoreThe Hacker News
Claude Used to Automate Exploitation and Data Theft Across Multiple Victims
Anthropic has warned that cybercriminals and state-sponsored hackers alike are using its Claude models for cyber attacks, weapons design, propaganda, and mass surveillance between December… Read MoreThe Hacker News
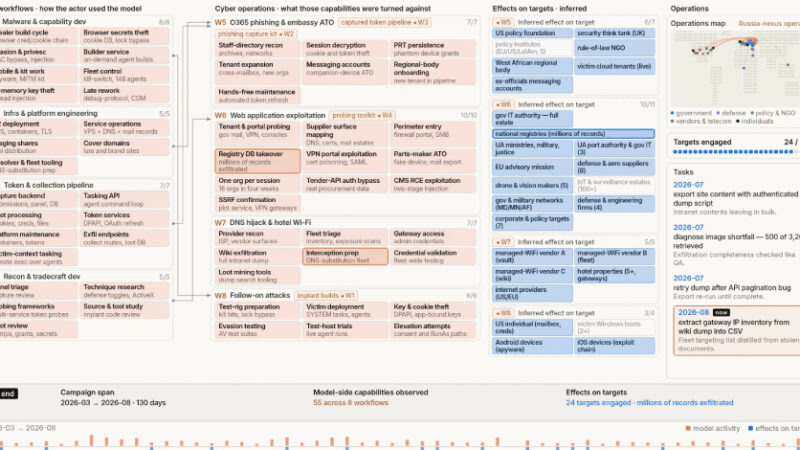
Russian State-Sponsored Hackers Use Claude to Rebuild Malware After Detection
Anthropic on Thursday revealed it disrupted a campaign mounted by a Russian state-sponsored threat actor that abused Claude for developing an AI-assisted workflow to get… Read MoreThe Hacker News
Attackers Chain JFrog Artifactory Flaws to Gain Admin Control and Plant Backdoors
Attackers have chained two flaws in JFrog Artifactory, the repository that software build pipelines pull from, to take administrator control of self-hosted servers and plant… Read MoreThe Hacker News
China-Linked UNC3569 Exploited Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
A China-linked hacking group exploited a flaw in Sogou Input Method, one of the most widely used tools for typing Chinese characters on Windows, to… Read MoreThe Hacker News