Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Microsoft Entra ID Flaw (CVSS 10.0) Exploited in Wild, Allows Remote Code Execution
Microsoft on Thursday warned of a maximum-severity security flaw in Entra ID that it said has been exploited in the wild, but noted that no… Read MoreThe Hacker News
Rust Supply Chain Attack Puts Build-Time Malware in Crates with 245 Million Downloads
The Rust Project has deleted malicious versions of three widely used Rust crates from crates.io after a compromised maintainer account published releases that added a… Read MoreThe Hacker News
Suspected Russian Hackers Abuse Google OAuth and WhatsApp Linking to Hijack Accounts
Three distinct suspected Russian cyber espionage threat clusters have been observed leveraging legitimate authentication flows to single out individuals working in academia, aerospace and defense,… Read MoreThe Hacker News
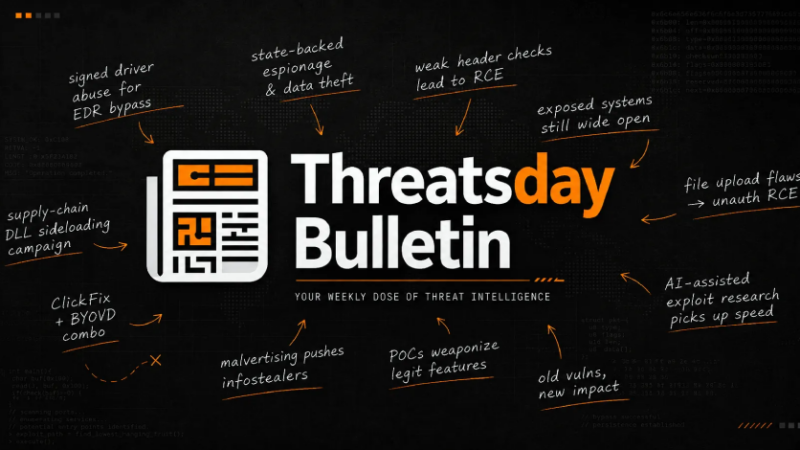
ThreatsDay: Gogs 10.0 RCE, n8n Workflow-to-RCE, $10M Reward, GLM-5.3 AI Exploit, and More
A lot of this week’s trouble starts with something trusted doing exactly what it was allowed to do. Signed drivers get turned against defenses. Legitimate… Read MoreThe Hacker News
Elementor Pro Flaw Could Let Unauthenticated Attackers Upload PHP and Execute Code
Cybersecurity researchers have disclosed details of a critical flaw in the Elementor Pro WordPress plugin that, if successfully exploited, could lead to remote code execution.… Read MoreThe Hacker News
Cloudflare Workers Spectre Attack Leaks JWT From Co-Located Worker at 12 Bits/Second
Cybersecurity researchers have disclosed details of a remote Spectre attack against Cloudflare Workers that leaked a JSON Web Token (JWT) from a co-located Worker in the production… Read MoreThe Hacker News
OpenAI Pauses Frontier RL Training as It Tightens Defenses Against Unsafe AI Behavior
OpenAI on Tuesday revealed that it paused reinforcement learning (RL) training for its latest artificial intelligence (AI) models for two weeks while it shored up… Read MoreThe Hacker News
SilkParasite Espionage Campaign Targets Central Asian Governments with Five New RATs
A previously unreported cyber espionage operation dubbed SilkParasite has been observed targeting government bodies in Central Asia. The intrusion set makes use of seven remote… Read MoreThe Hacker News
Hackers Compromised 14,500+ Dahua Devices Using Credential Attacks, Auth Bypasses, and P2P
Cybersecurity researchers at Hunt.io have disclosed details of a campaign that they say compromised more than 14,530 Dahua devices between June 17 and July 22,… Read MoreThe Hacker News
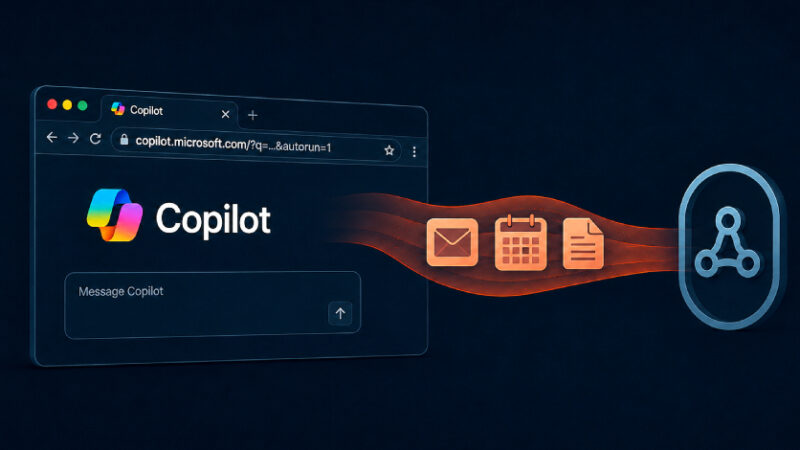
Microsoft Copilot Personal Flaws Could Let One Click Exfiltrate Data From Connected Apps
Varonis Threat Labs has disclosed three vulnerabilities in Microsoft Copilot Personal that it said could allow a single click on a crafted link to silently… Read MoreThe Hacker News