Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Articles By This Author
India Mandates Registered Caller Name Display on 4G and Newer Networks From November 1
The Indian government has directed telecom service providers (TSPs) in the country to mandatorily display callers’ registered names along with their numbers for incoming calls… Read MoreThe Hacker News
GhostAction Compromises About 1,900 GitHub Accounts, Targets Over 30,000 Repositories
The credential-theft campaign known as GhostAction has ramped up, targeting more than 30,000 repositories across 3,000 users and organizations. The spike, according to GitGuardian, was… Read MoreThe Hacker News
Langflow’s Critical Authenticated RCE Flaw Targeted in 1,423 Honeypot Exploit Attempts
Threat actors are exploiting a critical security flaw in Langflow, according to an alert from Previdian. Langflow is an open-source platform that allows developers to… Read MoreThe Hacker News
AhsayCBS Flaws Exploited to Deploy Web Shells Get New Fixes After Incomplete Patches
Singapore-based Ahsay Backup has released security updates to address two security flaws in AhsayCBS that have been exploited by bad actors to drop web shells… Read MoreThe Hacker News
Palo Alto Networks Patches PAN-OS Authenticated RCE Flaw Amid Active Exploitation
Palo Alto Networks on Wednesday issued security updates for a high-severity flaw in PAN-OS software that has come under active exploitation. The vulnerability, tracked as… Read MoreThe Hacker News
Researchers Used a Public OpenAI Model to Build a $250,000 Chrome Full-Chain Exploit in Six Days
A team at security firm XBOW chained three then-unknown Google Chrome bugs into a single attack that runs code on a Windows computer when the… Read MoreThe Hacker News
Hirudo Android Trojan Uses Patched Banking Apps to Bypass Their Built-In Security Checks
Cybersecurity researchers have disclosed details of a new Android banking trojan called Hirudo that works by replacing legitimate banking apps with purpose-built patched versions designed… Read MoreThe Hacker News
An AI Agent Found a Critical OTP Bypass in Production. The Attack Was the Easy Part.
The bug was simple: the login let you choose where your sign-in code went. Proving it on a live website was the hard part. TL;DR… Read MoreThe Hacker News
AI-Found Linux Kernel Flaw Gives Local Users Root, and Can Break a Guest Out to the Host
A flaw in Linux’s vhost subsystem lets a local user read and write kernel memory at will and become root across nearly a decade of… Read MoreThe Hacker News
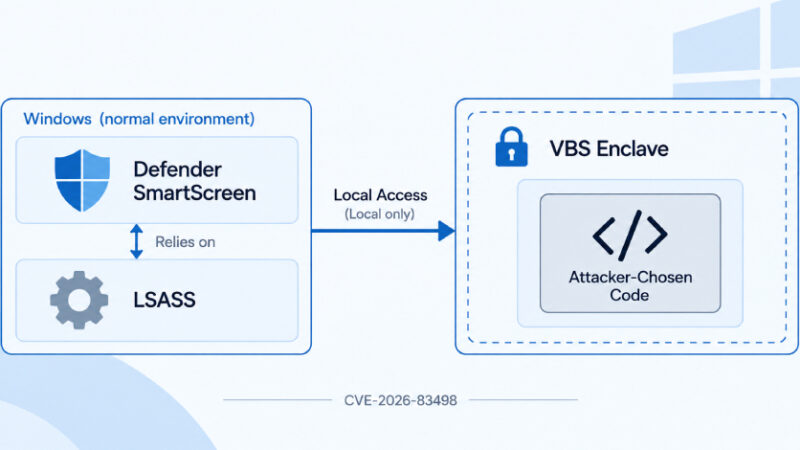
Four-Byte Write and Timing Bug Let Researchers Run Code in Windows SmartScreen Enclave
Security researchers ran their own code inside a protected part of Windows that is meant to stay sealed off even when the rest of the… Read MoreThe Hacker News