Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Articles By This Author
Fake ChatGPT, Gemini, and Claude Ad Portals Capture Credentials and MFA Codes
Cybersecurity researchers have disclosed details of a “human-operated phishing platform” that impersonates advertising products for artificial intelligence (AI) chatbots like Google Gemini, Anthropic Claude, OpenAI… Read MoreThe Hacker News
Linux Backdoors Impersonate Email Security Tools to Evade Detection in Korea and Taiwan
Linux backdoors targeting telecom and network appliances in South Korea and Taiwan have been disguising their traffic as email services and seemingly legitimate processes to… Read MoreThe Hacker News
LibreOffice and OpenOffice Flaws Let Malicious Spreadsheets Run Code Without Macro Warnings
A malicious spreadsheet can make LibreOffice and Apache OpenOffice run an attacker’s code as soon as the file is opened, security researchers have shown. There… Read MoreThe Hacker News
Google Pauses OSS Product Bug Bounty Rewards After Surge in Invalid Automated Reports
Google has stopped accepting product vulnerability reports through its bug bounty program for its open-source software. The change, in effect since October 1, means researchers… Read MoreThe Hacker News
Critical Atlassian Flaw Lets Unauthenticated Attackers Read Known Files Across 8 Products
A critical flaw in 8 Atlassian Data Center products, which customers host themselves, allows an attacker with no login access to read specific files in… Read MoreThe Hacker News
FBI Removes Accenture Contractor After Patch Failure Led to ShinyHunters Breach
The U.S. Federal Bureau of Investigation (FBI) has removed an Accenture contractor for their alleged role in a ShinyHunters-breach that led to the theft of… Read MoreThe Hacker News
Denmark Says Attackers Accessed CPR Data for 8.8 Million People via Company Account
Unauthorized parties have gained access to the names, addresses, and personal identification numbers of about 8.8 million people, living and dead, in Denmark’s national population… Read MoreThe Hacker News
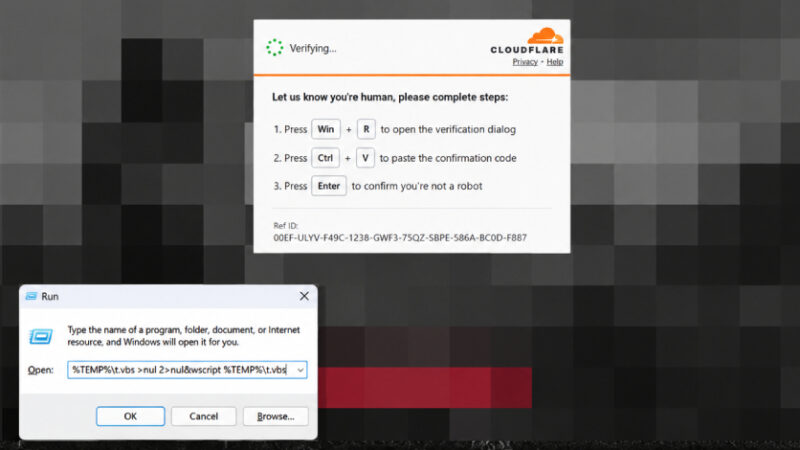
ClickFix Smuggles Payloads Through Browser Cache to Bypass Windows Run Limits
A new type of ClickFix attack is using compromised websites to trick users into executing a malicious payload cached in a web browser’s cache. “Instead… Read MoreThe Hacker News
Apple Plans Tighter macOS Full Disk Access Controls Over AI Agent Data Access
Apple has announced that it’s taking steps to tighten controls around a macOS setting called Full Disk Access (FDA) due to security risks posed by… Read MoreThe Hacker News
Attackers Target Rejetto HFS Flaw That Enables Admin Session Forgery and RCE
A critical security flaw impacting Rejetto HTTP File Server (HFS) is witnessing active exploitation attempts, according to VulnCheck. The vulnerability in question is CVE-2026-61500 (CVSS… Read MoreThe Hacker News