Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Articles By This Author
Zero Trust for AI Agents Starts With Fixing Zero Visibility
The way we talk about AI agents is shifting, and the way we implement them requires an even more fundamental shift. While earlier discourse focused… Read MoreThe Hacker News
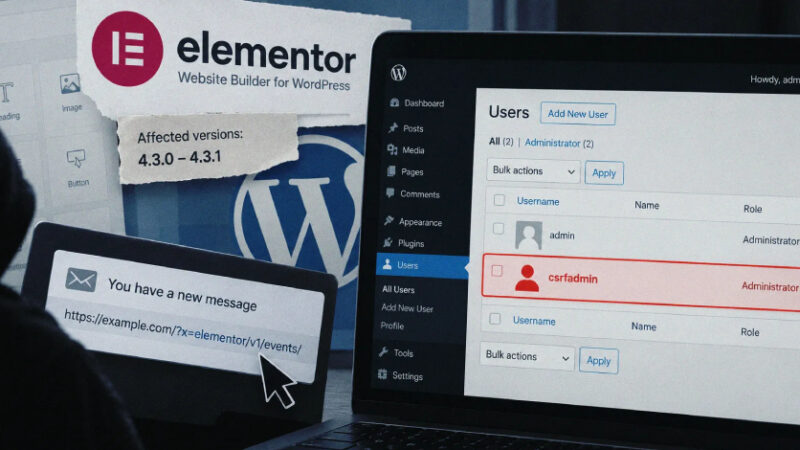
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create… Read MoreThe Hacker News
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities… Read MoreThe Hacker News
Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat… Read MoreThe Hacker News
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware
Two actions-cool GitHub Actions have been disabled for a second time after the repositories became accessible last week, months after they were compromised during the… Read MoreThe Hacker News
PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence
Cybersecurity researchers have flagged a new version of PamStealer that ensures that the main payload can only be recovered using a server-side decryption chain. The… Read MoreThe Hacker News
Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise
Cryptocurrency exchange Bitget said suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets. “At 18:31 UTC on September 24,… Read MoreThe Hacker News
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild
The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild. The vulnerability in question… Read MoreThe Hacker News
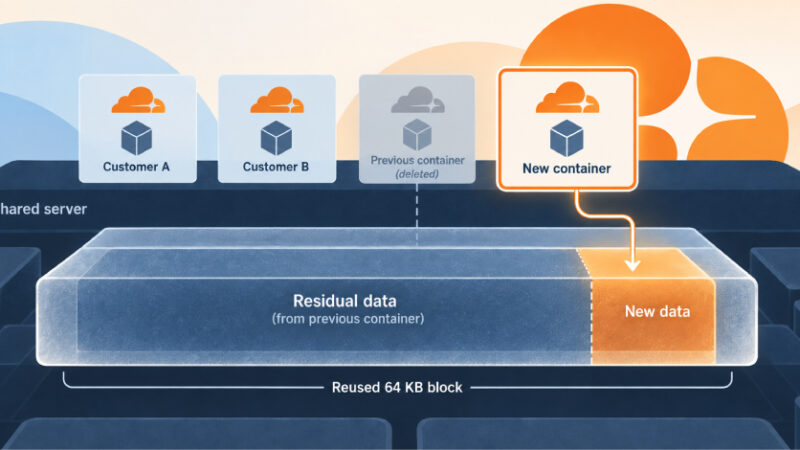
Cloudflare Fixes Flaw That Let One Container Read Another Customer’s Leftover Disk Data
A flaw in Cloudflare Containers let a paying customer read data that other customers’ containers had left behind on the same server, Cloudflare and the… Read MoreThe Hacker News
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added two critical security flaws impacting WSO2 and Adobe Commerce and Magento to its Known… Read MoreThe Hacker News