Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Articles By This Author
Microsoft Defender’s Own Driver Can Be Weaponized to Delete Security Software at Boot
Check Point Research has disclosed a technique that uses Microsoft Defender’s own legitimately signed boot-time remediation driver to perform arbitrary kernel-level file and registry operations… Read MoreThe Hacker News
Android Car Malware Spreads Through Built-In Updaters for Ad Fraud, Proxy Botnet
Cybersecurity researchers have flagged a new malware family that’s specifically designed to infect Android-based vehicle head unit firmware developed by DoFun. Kaspersky, which discovered the… Read MoreThe Hacker News
Wazuh and AI For Enhanced SOC Workflows
Artificial Intelligence (AI) has become one of this decade’s defining technologies. From healthcare and finance to manufacturing and education, organizations increasingly rely on AI to… Read MoreThe Hacker News
Cisco Patches Nine Crosswork and Secure Workload Flaws, Five Scoring CVSS 10.0
Cisco has published another round of security updates for Crosswork platforms and Secure Workload Software as part of a continued comprehensive internal security review. Four… Read MoreThe Hacker News
GitLab CVE-2026-19478 Comes Under Active Exploitation Within Days of Disclosure
A newly disclosed security flaw in GitLab has come under active exploitation within days of public disclosure, according to watchTowr. The vulnerability in question is… Read MoreThe Hacker News
Microsoft Entra ID Flaw (CVSS 10.0) Exploited in Wild, Allows Remote Code Execution
Microsoft on Thursday warned of a maximum-severity security flaw in Entra ID that it said has been exploited in the wild, but noted that no… Read MoreThe Hacker News
Rust Supply Chain Attack Puts Build-Time Malware in Crates with 245 Million Downloads
The Rust Project has deleted malicious versions of three widely used Rust crates from crates.io after a compromised maintainer account published releases that added a… Read MoreThe Hacker News
Suspected Russian Hackers Abuse Google OAuth and WhatsApp Linking to Hijack Accounts
Three distinct suspected Russian cyber espionage threat clusters have been observed leveraging legitimate authentication flows to single out individuals working in academia, aerospace and defense,… Read MoreThe Hacker News
ThreatsDay: Gogs 10.0 RCE, n8n Workflow-to-RCE, $10M Reward, GLM-5.3 AI Exploit, and More
A lot of this week’s trouble starts with something trusted doing exactly what it was allowed to do. Signed drivers get turned against defenses. Legitimate… Read MoreThe Hacker News
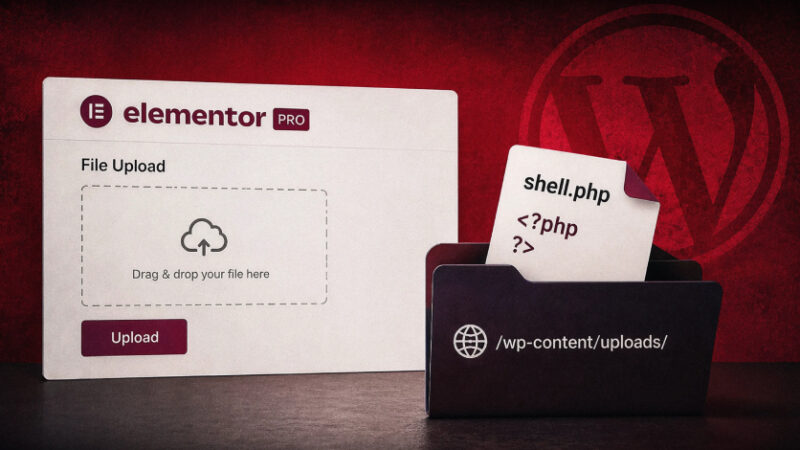
Elementor Pro Flaw Could Let Unauthenticated Attackers Upload PHP and Execute Code
Cybersecurity researchers have disclosed details of a critical flaw in the Elementor Pro WordPress plugin that, if successfully exploited, could lead to remote code execution.… Read MoreThe Hacker News