Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
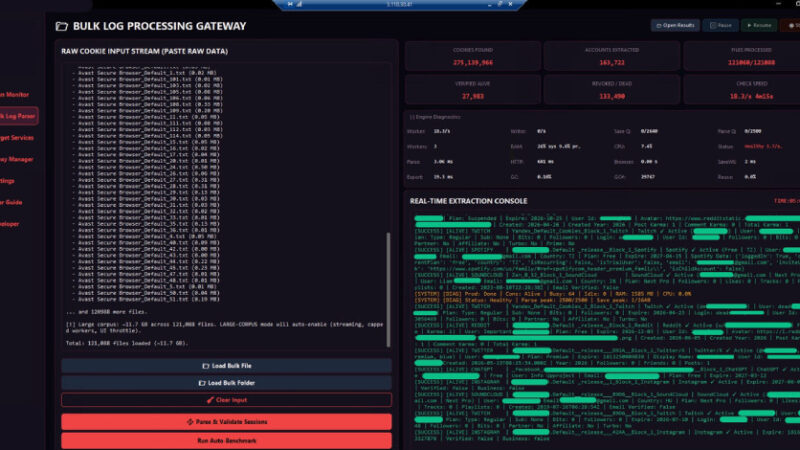
Infostealer Logs Expose Replayable AI Tokens That Can Bypass MFA
Cybercriminals are hijacking artificial intelligence (AI) user accounts via information stealer logs to create “stolen keys” that grant illicit access to tools from model providers… Read MoreThe Hacker News
Chrome V8 Zero-Day Exploited in the Wild Enables Code Execution Inside Sandbox
Google on Thursday released updates to patch 230 security vulnerabilities, including one that has come under active exploitation in the wild. The medium-severity vulnerability, assigned… Read MoreThe Hacker News
New cPanel Flaw Lets a Hosting Account With Mail Privileges Run Code as Root
cPanel has patched a flaw that it says lets a single hosting account take control of an entire server. An authenticated account holder with mail-related… Read MoreThe Hacker News
F5 BIG-IP APM Malware Injects a PHP Web Shell Into Memory, Evading Disk Scans
Malware linked to break-ins at F5 BIG-IP Access Policy Manager appliances hides a PHP web shell in memory instead of in a file on disk,… Read MoreThe Hacker News
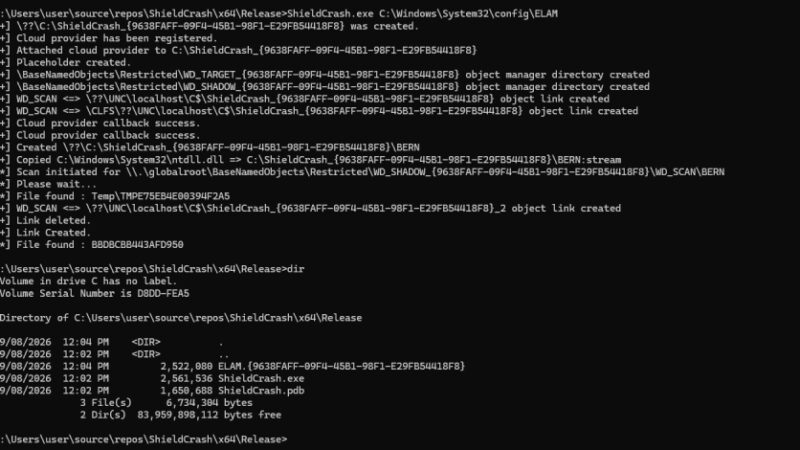
Researcher Drops New Microsoft Defender PoC Showing ShieldBreak Patch Can Be Bypassed
The security researcher known as Chaotic Eclipse has dropped a proof-of-concept (PoC) for yet another zero-day in Microsoft Defender. The vulnerability, codenamed ShieldCrash, is assessed… Read MoreThe Hacker News
SAP Patches CVSS 10.0 Kernel Flaw Enabling Unauthenticated Remote Code Execution
SAP has released security updates to address multiple vulnerabilities, including a maximum-severity flaw in SAP Extended Passport (EPP) Processing that could have a severe impact… Read MoreThe Hacker News
Adobe Patches Magento Zero-Day Exploited to Deploy Rust Backdoor and PHP Web Shell
Adobe on Monday released security patches to address a maximum-severity flaw impacting Adobe Commerce and Magento Open Source that has come under active exploitation in the wild.… Read MoreThe Hacker News
BengalSEO Poisons Bing Search Results to Deliver MayaBot and Tech Support Scams
Cybersecurity researchers have disclosed details of a sprawling search engine optimization (SEO) poisoning campaign that paves the way for malware deployment and tech support scams.… Read MoreThe Hacker News
Grindr to Pay £26 Million to Settle U.K. Claims Over HIV Status Data Sharing
Online dating app Grindr has opted to pay £26 million ($35.1 million) to settle a lawsuit in the U.K. over allegations that it shared users’… Read MoreThe Hacker News
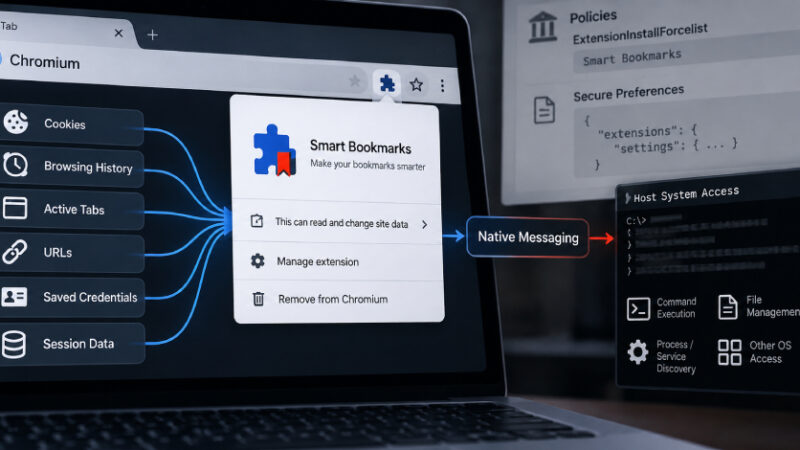
PEEP Turns Chrome and Edge Into Post-Compromise Backdoors for Host Command Execution
Cybersecurity researchers have disclosed details of a complex Chromium-based post-exploitation toolkit called PEEP that masquerades as a bookmarks extension for the web browser. “Requiring prior… Read MoreThe Hacker News