Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
PamStealer macOS Malware Adds Live C2 Payload Decryption and Multi-Layer Persistence
Cybersecurity researchers have flagged a new version of PamStealer that ensures that the main payload can only be recovered using a server-side decryption chain. The… Read MoreThe Hacker News
Bitget Says Suspected North Korean Hackers Stole $351.6M After Backend Compromise
Cryptocurrency exchange Bitget said suspected North Korean threat actors have stolen $351.6 million from its hot and warm wallets. “At 18:31 UTC on September 24,… Read MoreThe Hacker News
Roundcube Pre-Auth SQL Injection Flaw Actively Exploited in the Wild
The Canadian Centre for Cyber Security has warned that a now-patched Roundcube Webmail vulnerability is being actively exploited in the wild. The vulnerability in question… Read MoreThe Hacker News
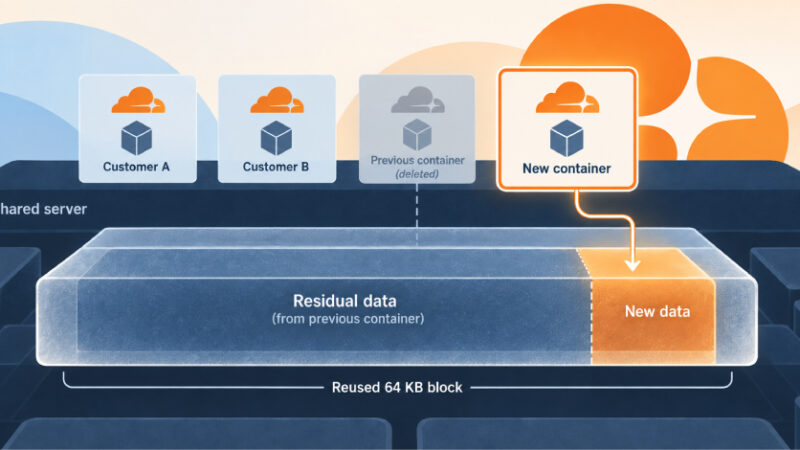
Cloudflare Fixes Flaw That Let One Container Read Another Customer’s Leftover Disk Data
A flaw in Cloudflare Containers let a paying customer read data that other customers’ containers had left behind on the same server, Cloudflare and the… Read MoreThe Hacker News
WSO2 and Adobe Commerce Flaws Exploited in Attacks, Added to CISA KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA), on Thursday, added two critical security flaws impacting WSO2 and Adobe Commerce and Magento to its Known… Read MoreThe Hacker News
Unpatched OnePlus Flaws Let Installed Android Apps Gain Root Without Permissions
A OnePlus 15 running the latest OxygenOS can be rooted by a malicious app the owner installs, one that asks for no special permissions. A… Read MoreThe Hacker News
17,000 URLs Reveal How ClickFix Turns Trusted Websites Into Malware Traps: Report by CTM360
ClickFix has become the most common way attackers get into enterprise networks, and it does it without an exploit, an attachment, or a file on… Read MoreThe Hacker News
OpenAI Agent Bypassed Australian Medicare Portal Controls to Access Non-Public Files
An AI agent on an internal OpenAI research task bypassed access controls on an Australian government Medicare statistics portal in June, Prime Minister Anthony Albanese said.… Read MoreThe Hacker News
TeamFiltration Campaign Compromises Seven Microsoft 365 Accounts Using Default Passwords
Cybersecurity researchers have disclosed details of an active TeamFiltration campaign codenamed UNK_CondorFiltration that has targeted over 5,700 accounts across 28 Microsoft 365 tenants. According to… Read MoreThe Hacker News
Attackers Exploit WordPress CVE-2026-87902 Within Hours of Disclosure
Threat actors have begun to actively exploit a critical security flaw in WordPress within hours of public disclosure. The vulnerability in question is CVE-2026-87902 (CVSS… Read MoreThe Hacker News