Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
JADEPUFFER-Linked Attackers Used Compromised Service Principals to Delete Azure Resources
The threat actor known as JADEPUFFER has been observed orchestrating destructive actions within a Microsoft Azure environment using compromised service principals. Microsoft, which is tracking… Read MoreThe Hacker News
CISA Says Attackers Are Exploiting Two Critical Citrix NetScaler Flaws Globally
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Sunday added two critical Citrix NetScaler ADC and Gateway flaws to its Known Exploited Vulnerabilities (KEV)… Read MoreThe Hacker News
Warning: Two Unpatched Citrix NetScaler RCE Zero-Days Under Active Exploitation
Two new unpatched zero-day vulnerabilities in Citrix NetScaler ADC and NetScaler Gateway appliances that allow remote code execution are being actively exploited in the wild,… Read MoreThe Hacker News
Lunex Stealer Abuses AMD Driver to Disable Security Monitoring and Steal Browser Credentials
The Psychedelic Stealer malware distributed via compromised Ukrainian websites using ClickFix-style Cloudflare verification checks is part of a wider malware-as-a-service (MaaS) platform called Lunex. The… Read MoreThe Hacker News
Attackers Bypass WAFs to Exploit Oracle PeopleSoft Flaw and Deploy Web Shells
Google is warning of renewed mass exploitation of a known security vulnerability in Oracle PeopleSoft as part of a campaign targeting multiple sectors globally. The… Read MoreThe Hacker News
Zero Trust for AI Agents Starts With Fixing Zero Visibility
The way we talk about AI agents is shifting, and the way we implement them requires an even more fundamental shift. While earlier discourse focused… Read MoreThe Hacker News
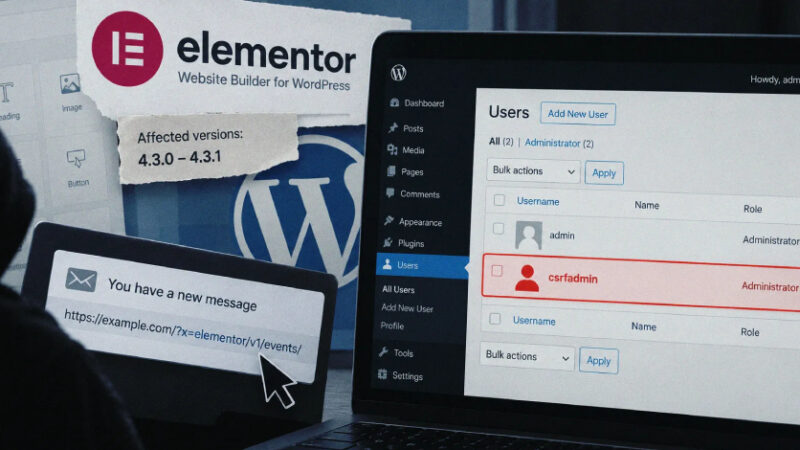
Elementor CSRF Flaw Lets Attackers Take Over Sites After Admin Clicks Crafted Link
Details have emerged about a high-severity security flaw in the Elementor Website Builder WordPress plugin that could be exploited by an unauthenticated attacker to create… Read MoreThe Hacker News
SharePoint RCE and MikroTik RouterOS Flaws Actively Exploited in the Wild
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) on Friday added two security flaws impacting Microsoft SharePoint and Mikrotik RouterOS to its Known Exploited Vulnerabilities… Read MoreThe Hacker News
Kiteworks Urges Customers to Shut Down Systems for 9 Hours Over Possible Cyber Attack
Kiteworks (formerly Accellion) is urging customers to shut down their systems as a precautionary measure for nine hours over the weekend after it received threat… Read MoreThe Hacker News
Compromised GitHub Actions Came Back Online and Resumed Executing Mini Shai-Hulud Malware
Two actions-cool GitHub Actions have been disabled for a second time after the repositories became accessible last week, months after they were compromised during the… Read MoreThe Hacker News