Smart, Real-Time Protection for Your Digital Life. Because your digital life is different from ordinary people.
Attacker Hijacks AI Coding Assistant Session, Spreads Shai-Hulud Across About 100 Repositories
Mandiant says an attacker hijacked an active AI coding-assistant session at an unnamed software-as-a-service provider and later spread Shai-Hulud across about 100 internal code repositories. Before the… Read MoreThe Hacker News
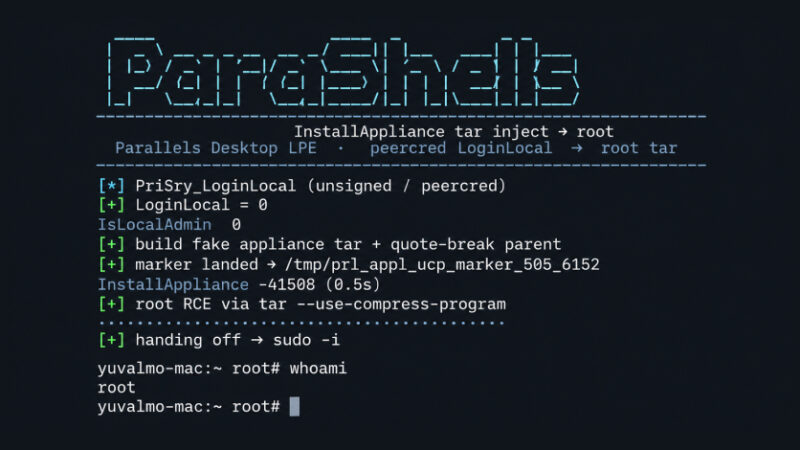
Parallels Desktop Flaw Lets Non-Admin Mac Users Gain Root, but Intel Macs Can’t Install Fix
Parallels Desktop for Mac has a flaw that lets an ordinary local account run code as root, the highest level of access on a Mac,… Read MoreThe Hacker News
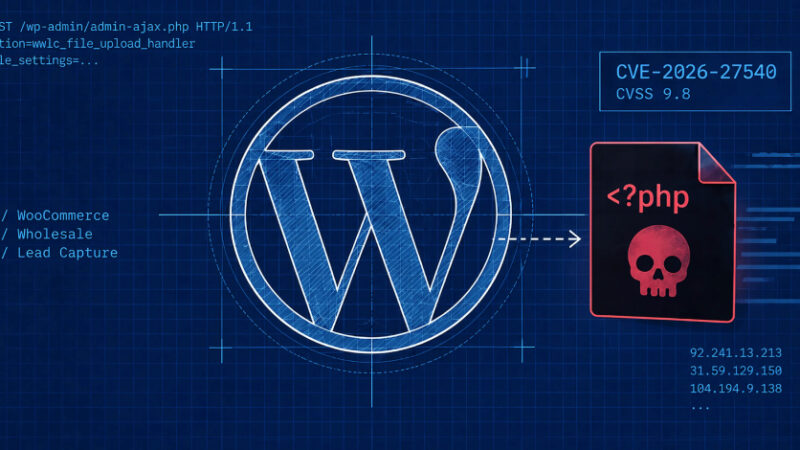
Attackers Exploit WooCommerce Wholesale Lead Capture Flaw to Plant PHP Web Shells
Threat actors are exploiting a critical security flaw in WooCommerce Wholesale Lead Capture, a premium WordPress plugin that has more than 6,000 active installs. “This… Read MoreThe Hacker News
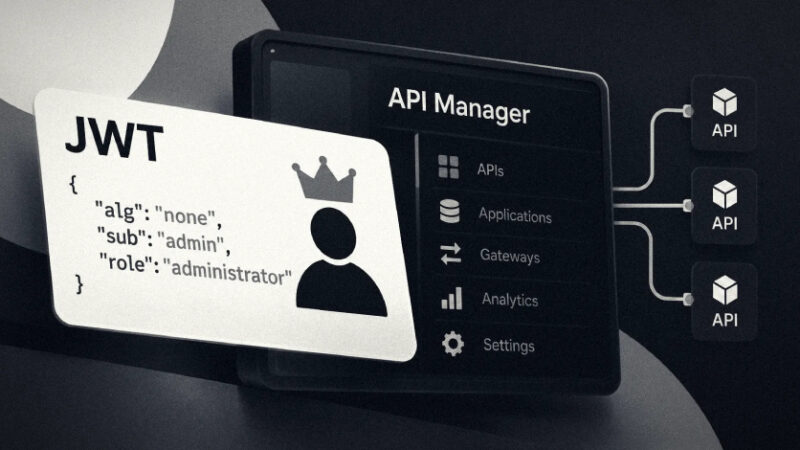
Active Exploitation Attempts Target WSO2 API Manager JWT Bypass With Forged Admin Tokens
A critical security flaw in WSO2 API Manager has come under active exploitation in the wild, according to findings from watchTowr. The vulnerability, tracked as… Read MoreThe Hacker News
KREMLIN Banking Malware Hijacks Chrome and Edge to Steal Credentials and Session Tokens
Cybersecurity researchers have shed light on a previously undocumented Brazilian banking malware operation that delivers a toolkit called KREMLIN. Elastic Security Labs is tracking the… Read MoreThe Hacker News
Iranian Hackers Use Telegram-Controlled Malware to Spy on Dissidents and Journalists
Cybersecurity agencies in the United States, the United Kingdom, and the Netherlands have detailed a Windows malware that they say Iran’s intelligence service uses to… Read MoreThe Hacker News
BambooToken Malware Uses MQTT to Control Windows and Linux Systems
Cybersecurity researchers have disclosed details of a multi-platform campaign that uses the Message Queueing Telemetry Transport (MQTT) protocol as a communication channel to control Windows… Read MoreThe Hacker News
LiteSpeed Enterprise Flaw Could Let One Hosting Account Gain Root Access on a Shared Server
A critical vulnerability in LiteSpeed Web Server Enterprise could let a low-privilege website user gain root access on a shared-hosting server, cPanel warned in an advisory… Read MoreThe Hacker News
Cisco Secure Email Gateway Flaw Exploited in the Wild, Enables Root Command Execution
Cisco has warned that a new critical vulnerability impacting AsyncOS Software for Cisco Secure Email Gateway has come under active exploitation in the wild. The… Read MoreThe Hacker News
China-Linked Hackers Exploit Chrome-Windows Zero-Day Chain to Deploy GRIMWEDGE
A Chinese threat actor has been attributed to a spear-phishing campaign that exploits recently patched security flaws in Google Chrome and Microsoft Windows to deliver… Read MoreThe Hacker News